Capture The Flag
(CTF)
What is a CTF
2
Capture The Flag
Capture the flag is a gamified cybersecurity competition designed
to challenge people to solve security problems. It’s a way you
learn penetration testing (ethical hacking).
3
How does a CTF look like ?
It’s like a puzzle where you will need to find vulnerabilities in web
application or in a system (linux/windows). You will “hack” your way
in to a server using the vulnerabilities you find.
Types of CTF
There are 3 types of CTF which helps you to gain practical skills
in solving something , you will not only talk about security but you
will do hands on hacking.
◩ Jeopardy
◩ Attack and Defense
◩ Boot2Root
4
Jeopardy
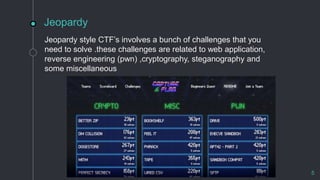
Jeopardy style CTF’s involves a bunch of challenges that you
need to solve .these challenges are related to web application,
reverse engineering (pwn) ,cryptography, steganography and
some miscellaneous
5
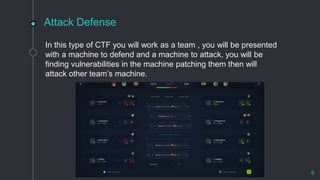
Attack Defense
In this type of CTF you will work as a team , you will be presented
with a machine to defend and a machine to attack, you will be
finding vulnerabilities in the machine patching them then will
attack other team’s machine.
6
Boot2Root
In this type you will presented with a machine which we call it a
“black box” , you don’t know what’s in their , which type of
operating system it is , what is running on that machine , ports ,
application and so on.
7
Are CTF’s applicable in real life
scenarios ?
8
How can we gain real life experience ?
◩ Doing a pentest of enterprise companies , start up companies
and etc.
◩ Doing bug bounties on public/private programs like facebook
, netflix, snapchat and etc through bug bounty platforms like
Hackerone, Bugcrowd and intigriti.
9
Tools used in CTF’s /Bug bounties
◩ Burpsuite
◩ Nmap
◩ Hashcat
◩ Sqlmap
◩ Metasploit
◩ Msfvenom
◩ Gobuster
◩ Ghidra
◩ Custom tools/scripts
10
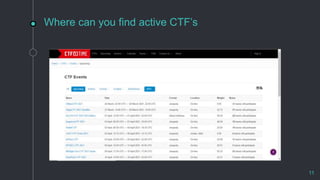
Where can you find active CTF’s
11
How can you get better at CTF’s ?
12