The document discusses security best practices for IBM Informix including:
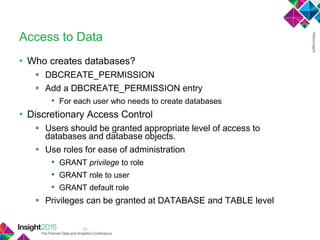
1) Enabling role separation to restrict access and privileges for database administrators, application administrators, and backup administrators.
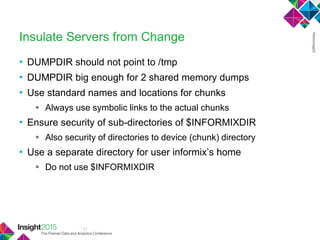
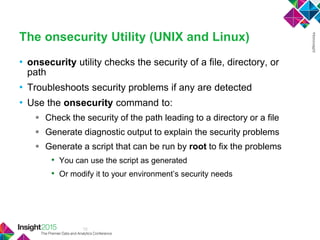
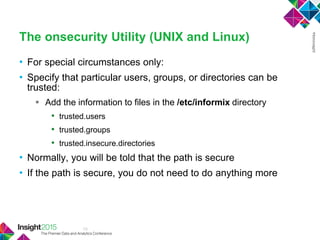
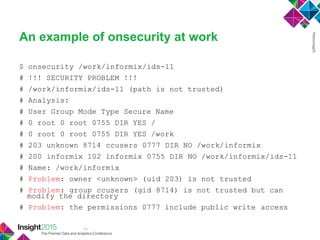
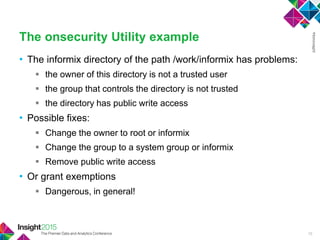
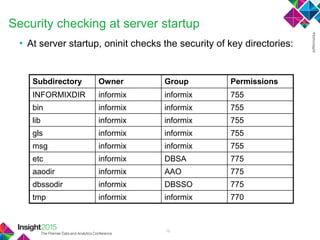
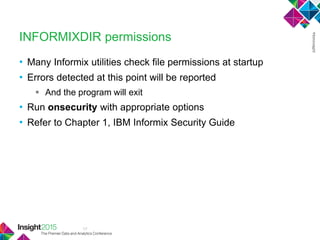
2) Configuring file permissions and ownership for key Informix directories and files to restrict access.
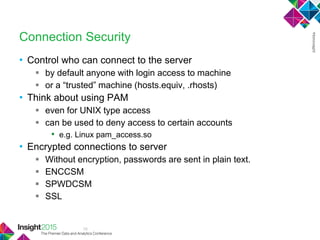
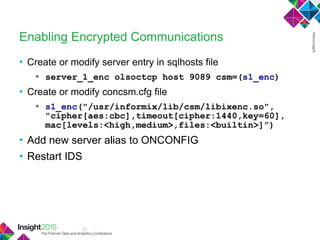
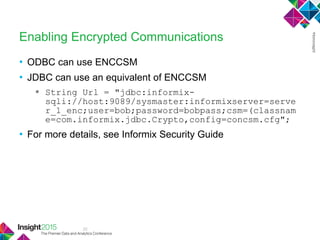
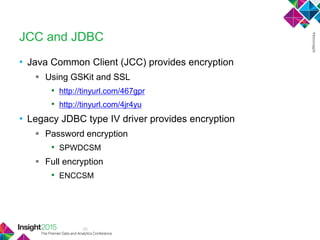
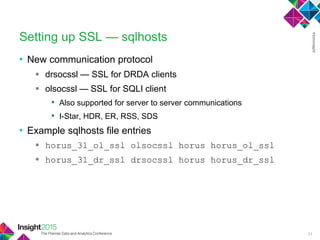
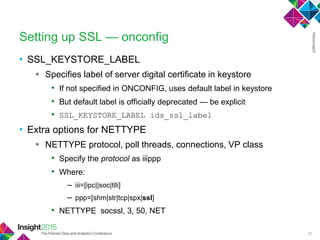
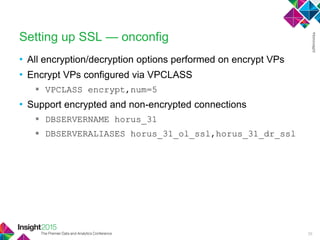
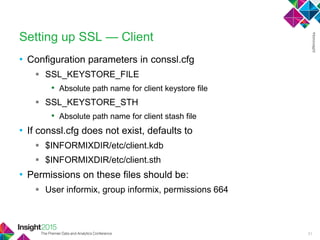
3) Enabling encrypted connections using SSL or other encryption mechanisms to protect data in transit.
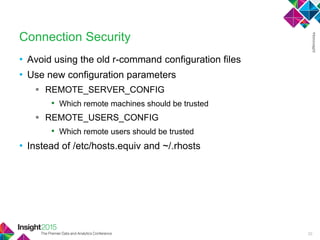
4) Configuring firewalls, virtual private networks, and the sqlhosts file to control which clients and users can connect to the database server.
 Most read
 Most read
 Most read