Download as PDF, PPTX
- 1 / 52
- 2 / 52
- 3 / 52
- 4 / 52
- 5 / 52
- 6 / 52
- 7 / 52
- 8 / 52
- 9 / 52
- 10 / 52
- 11 / 52
- 12 / 52
- 13 / 52
- 14 / 52
- 15 / 52
- 16 / 52
- 17 / 52
- 18 / 52
- 19 / 52
- 20 / 52
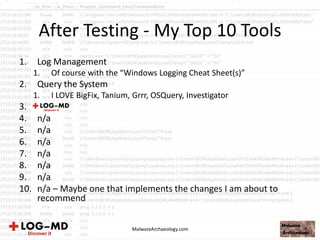

This document discusses the presenter's testing of various EDR and EPP solutions using three malware samples. Key findings include: 1) Many solutions failed to detect infections, even those detected by the presenter's IPS. Detection was weakest for "fileless" Kovter and morphing Dridex malware. 2) Solutions provided inadequate details to fully remediate infections. The presenter's own LOG-MD tool outperformed EDR solutions in revealing infection artifacts. 3) Based on the results, the presenter recommends that EDR tools integrate capabilities to remotely run third-party tools like LOG-MD for more thorough investigations. Simpler consoles are also needed to distribute workload across security


