Downloaded 373 times
- 1 / 61
- 2 / 61
- 3 / 61
- 4 / 61
- 5 / 61
- 6 / 61
 Most read
- 7 / 61
- 8 / 61
- 9 / 61
- 10 / 61
- 11 / 61
- 12 / 61
 Most read
- 13 / 61
- 14 / 61
- 15 / 61
- 16 / 61
- 17 / 61
- 18 / 61
- 19 / 61
- 20 / 61
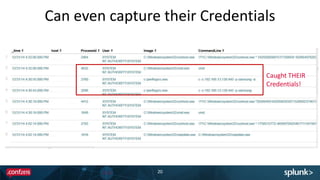
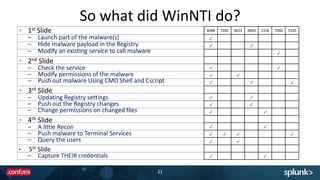
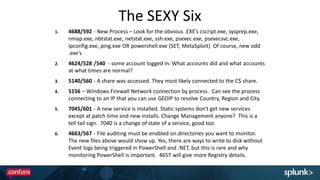
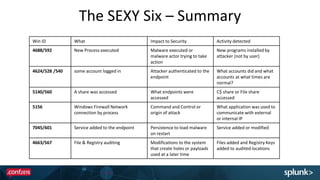
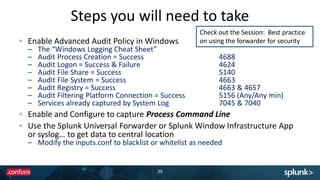
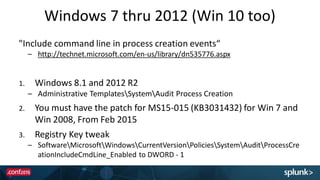
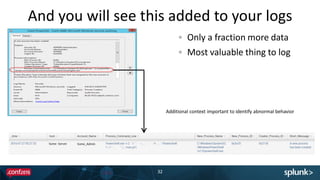
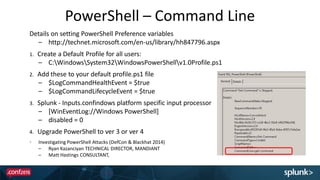
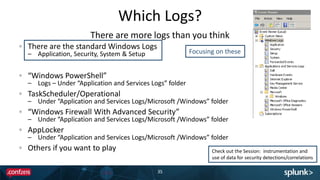
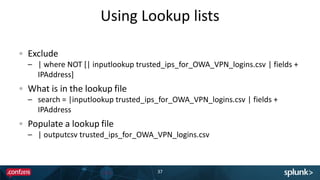
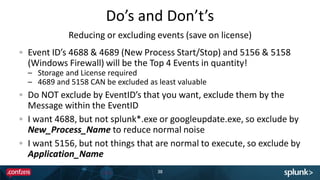
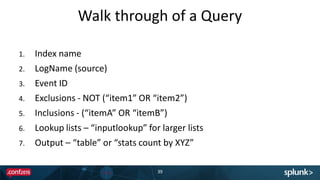
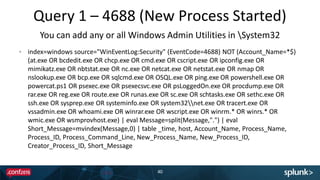
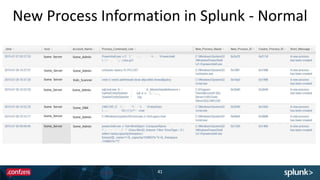
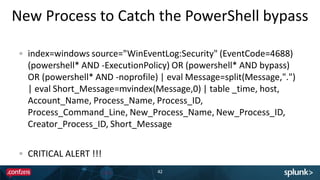
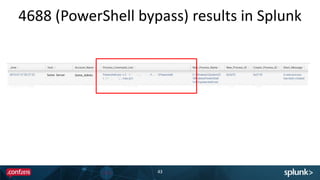
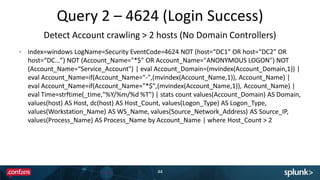
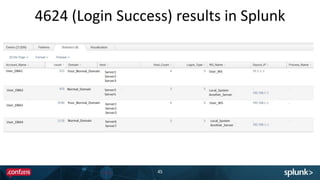
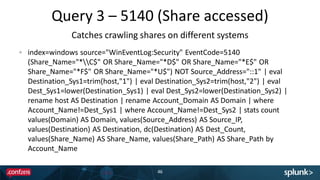
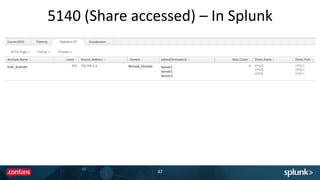
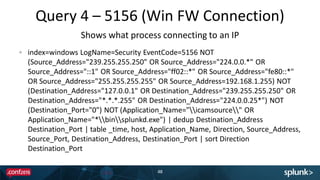
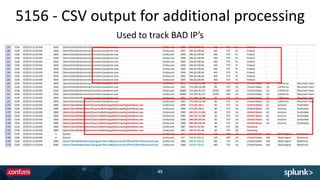
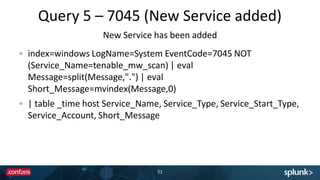
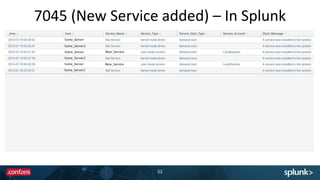
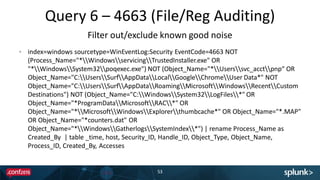
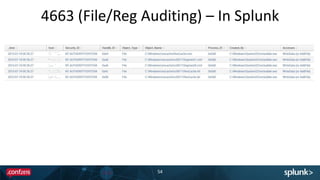
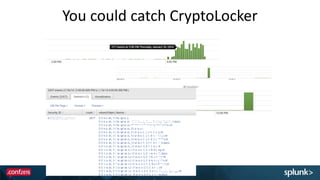
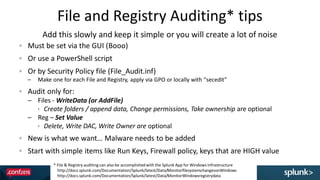
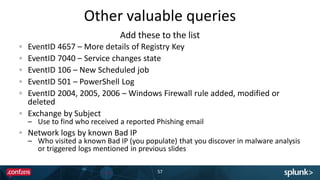
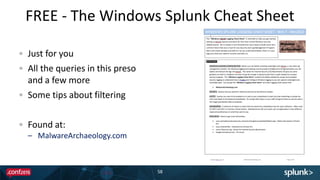
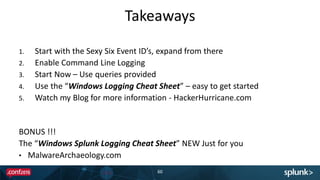

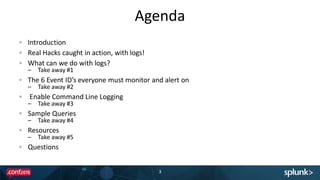
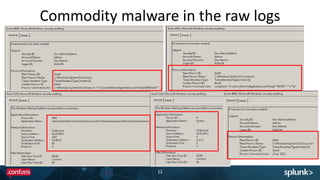
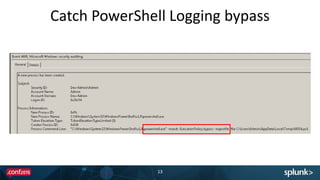
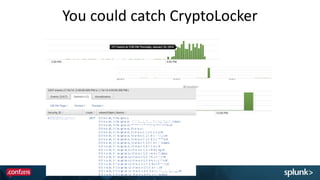
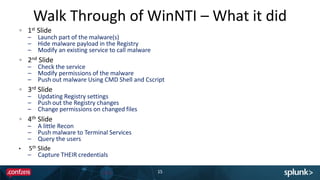
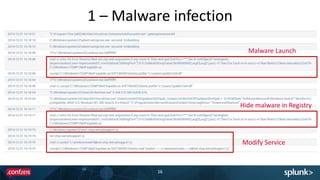
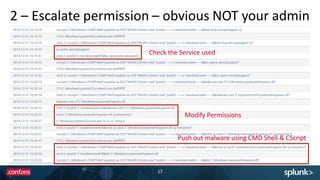
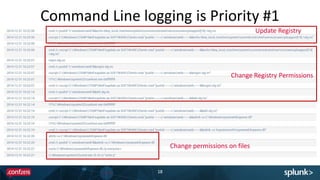
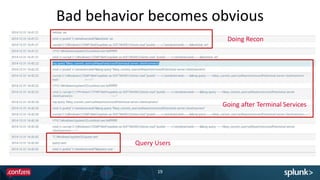
The document discusses using Windows event logs to detect advanced attacks and malware. It provides the following key points: 1. Six main Windows event IDs (4688, 4624, 5140, 5156, 7045, 4663) can be monitored and alerted on to detect a variety of malware and hacker activity. 2. Real examples are shown of how logs caught commodity malware, PowerShell logging bypasses, and the multi-stage WinNTI attack in action. 3. Tips are provided on enabling command line logging, using lookup lists to reduce noise, and sample Splunk queries to analyze key events like new processes started and logon activity. 4. Attendees


