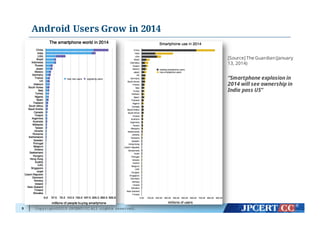
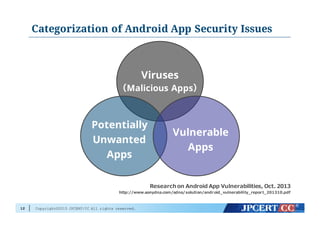
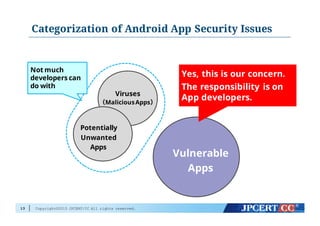
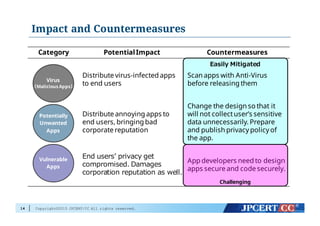
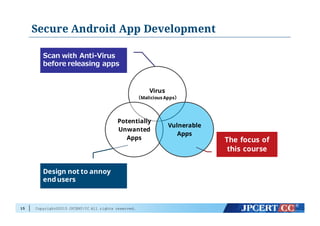
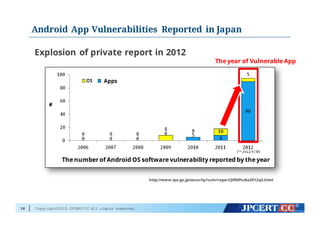
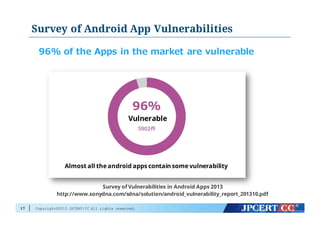
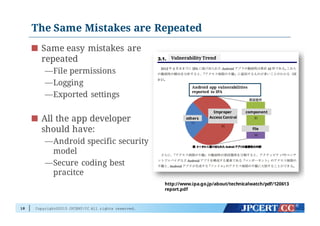
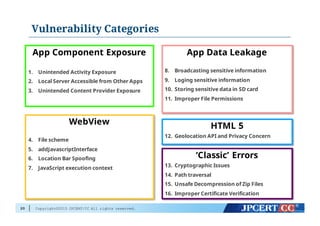
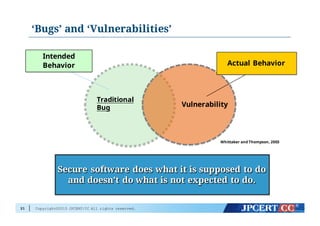
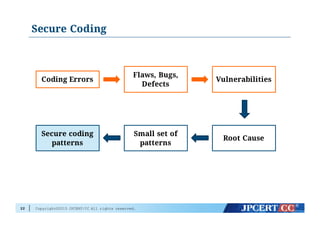
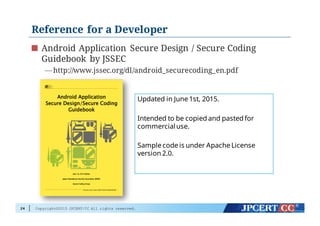
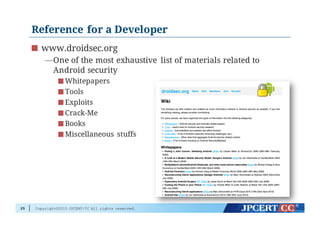
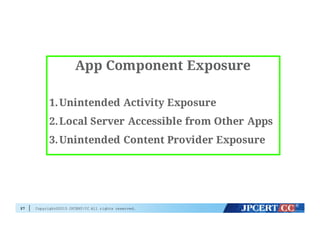
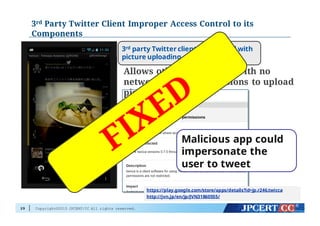
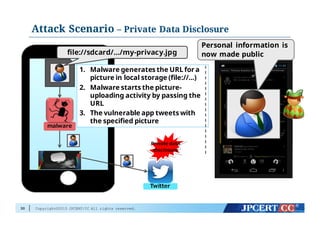
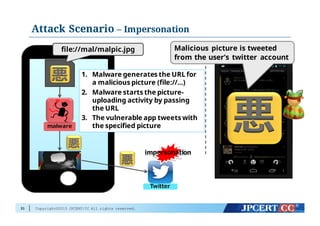
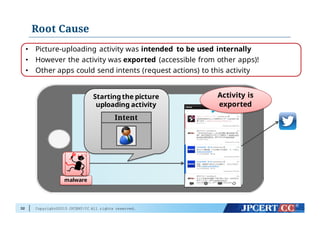
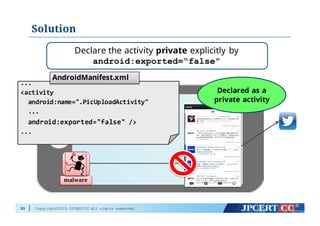
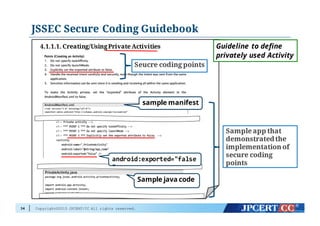
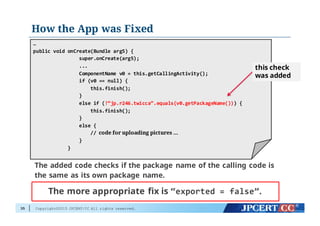
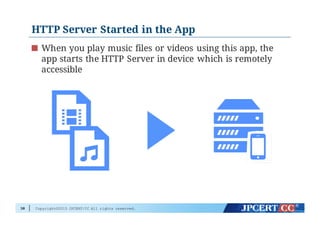
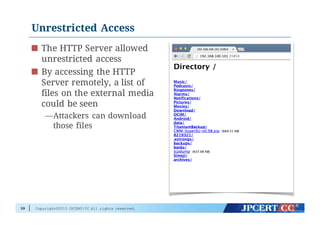
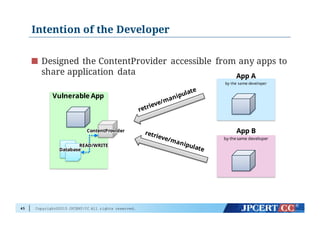
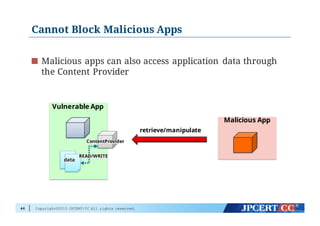
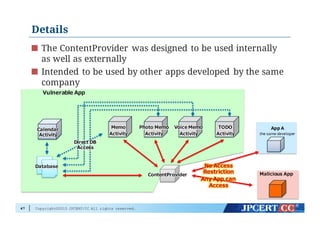
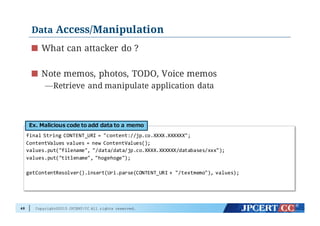
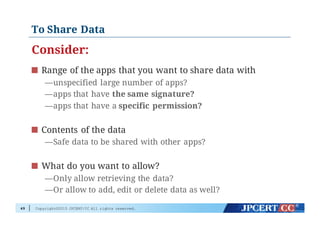
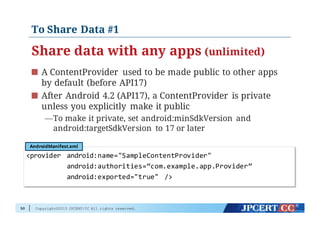
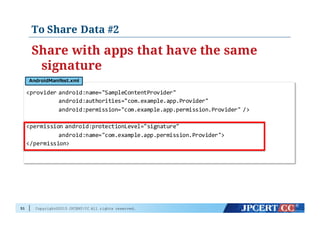
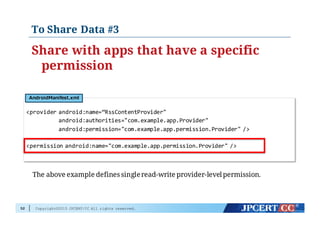
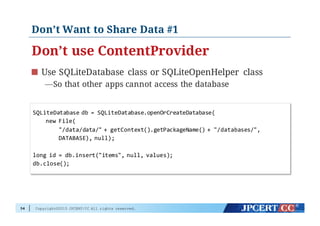
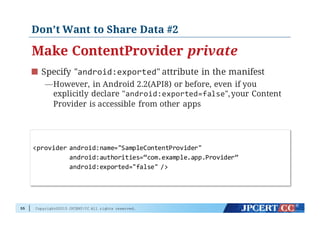
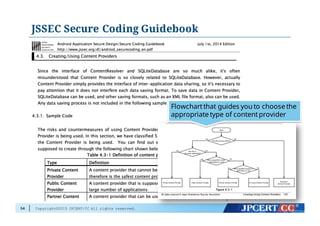
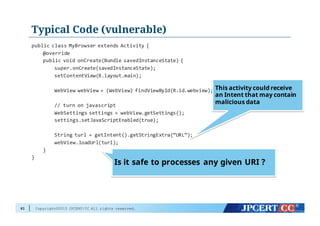
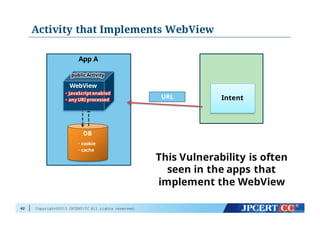
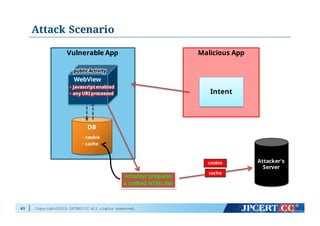
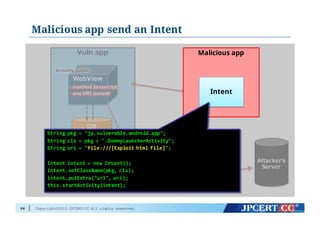
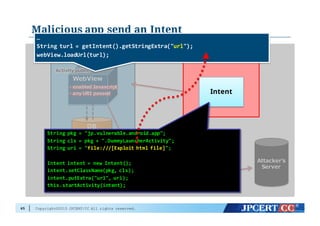
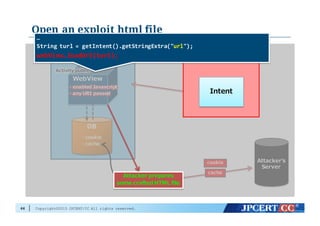
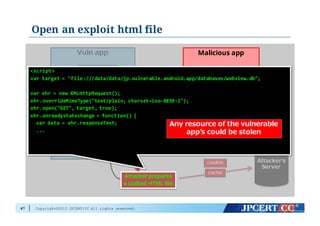
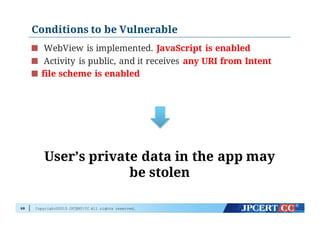
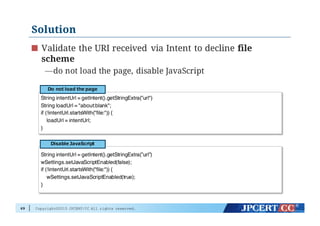
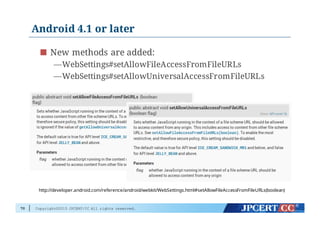
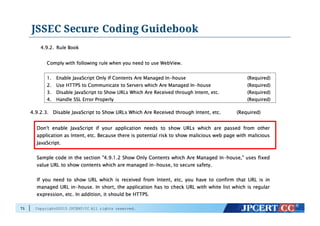
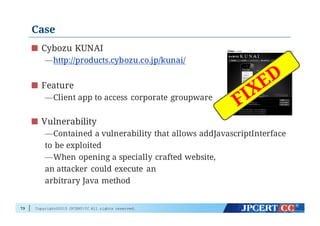
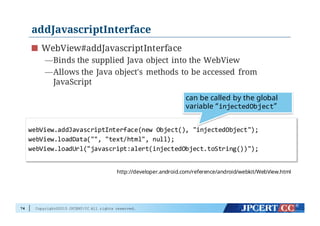
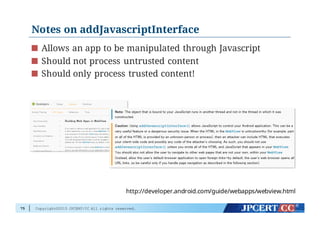
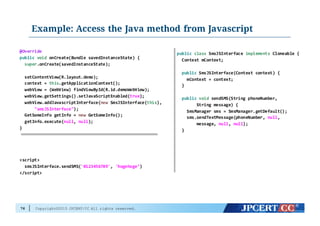
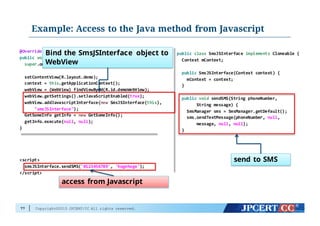
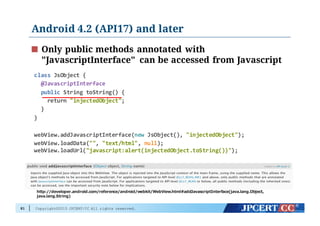
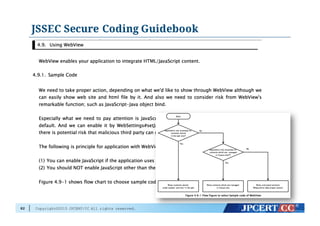
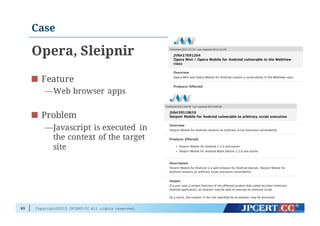
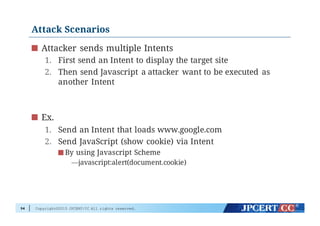
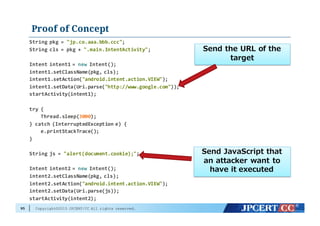
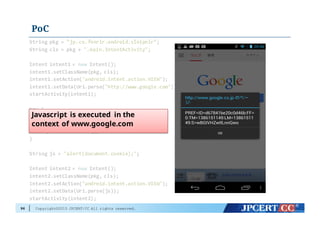
The document discusses secure coding practices for Android app development. It begins with an introduction that notes the growing number of Android users and prevalence of Android vulnerabilities reported in news headlines. The document then covers various categories of Android app security issues and explores examples of specific vulnerabilities, including unintended activity exposure, local servers accessible to other apps, and unintended content provider exposure. Root causes and solutions are provided for each vulnerability along with references for developers. The goal is to help developers learn from real-world examples and avoid common vulnerabilities through secure coding techniques.