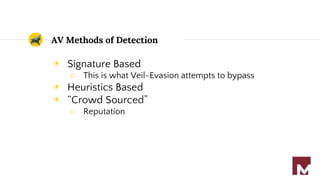
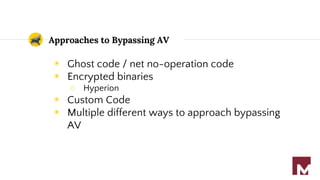
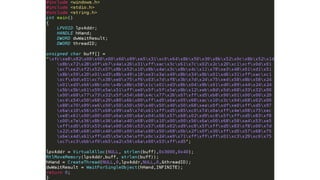
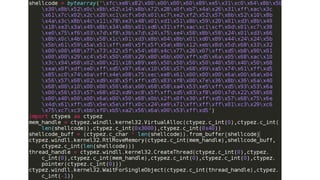
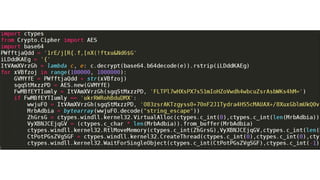
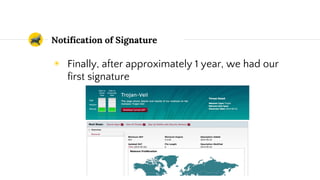
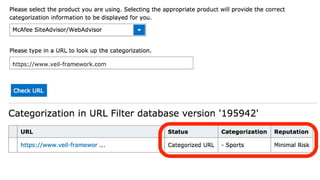
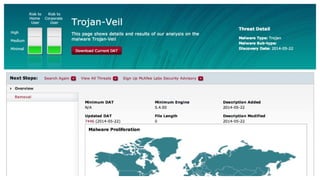
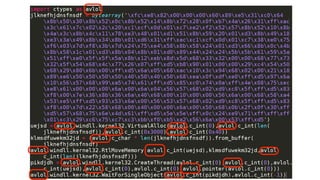
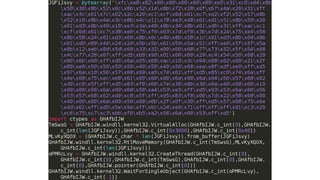
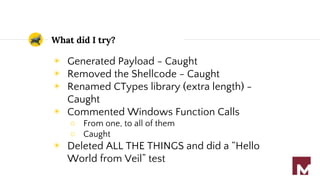
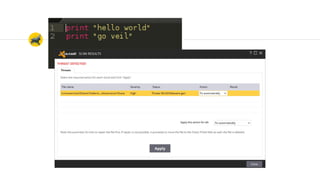
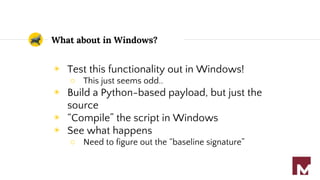
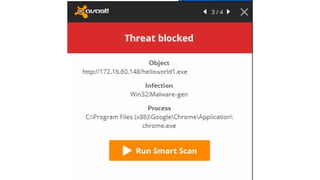
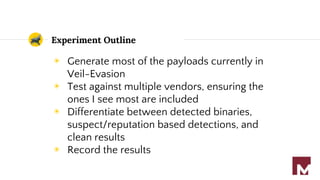
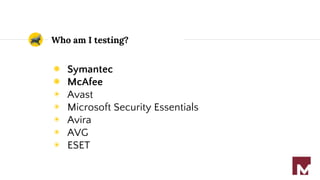
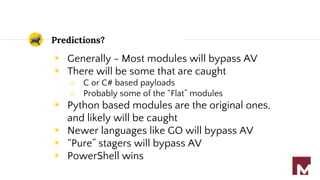
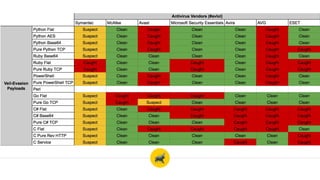
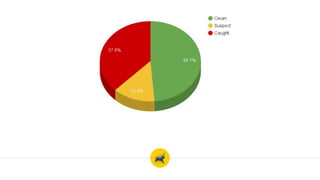
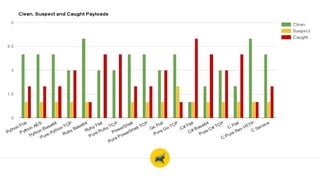
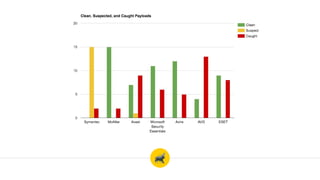
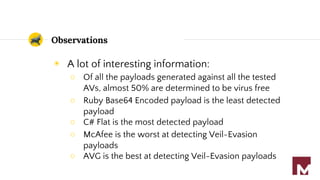
The document discusses techniques for bypassing antivirus (AV) detection using veil-evasion and stager concepts, focusing on methods such as code obfuscation and using non-standard programming languages for payload generation. It highlights a variety of AV detection methodologies, experiments conducted on multiple AV vendors, and findings revealing differences in their effectiveness against generated payloads. The author emphasizes that minor modifications can lead to successful bypassing of AVs and encourages a process-oriented approach to engaging with unknown technologies.