Shared 
Responsibility 
Mark Nunnikhoven 
@marknca 
…In Action
MODELLING 
SECURITY 
on AWS
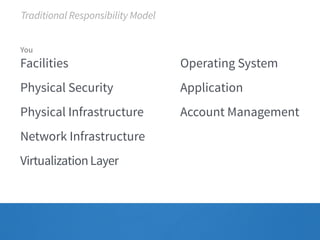
Traditional Responsibility Model 
! 
Operating System 
Application 
Account Management 
You 
Facilities 
Physical Security 
Physical Infrastructure 
Network Infrastructure 
Virtualization Layer
Shared Responsibility Model 
You 
Operating System 
Application 
Account Management 
Security Groups 
Network Configuration 
AWS 
Facilities 
Physical Security 
Physical Infrastructure 
Network Infrastructure 
Virtualization Layer 
More info on the model is available at http://aws.amazon.com/security
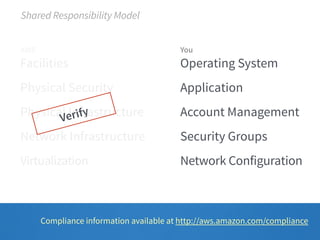
Shared Responsibility Model 
You 
Operating System 
Application 
Account Management 
Security Groups 
Network Configuration 
AWS 
Facilities 
Physical Security 
Physical Verify 
Infrastructure 
Network Infrastructure 
Virtualization 
Compliance information available at http://aws.amazon.com/compliance
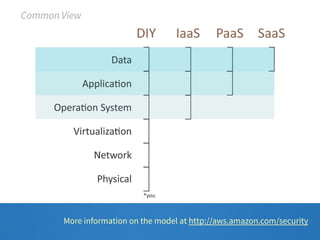
Common View 
More information on the model at http://aws.amazon.com/security
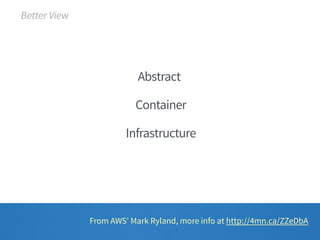
Abstract 
Container 
Infrastructure 
Better View 
From AWS’ Mark Ryland, more info at http://4mn.ca/ZZeDbA
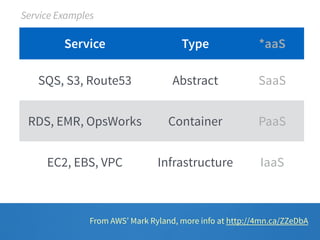
Service Examples 
Service Type *aaS 
SQS, S3, Route53 Abstract SaaS 
RDS, EMR, OpsWorks Container PaaS 
EC2, EBS, VPC Infrastructure IaaS 
From AWS’ Mark Ryland, more info at http://4mn.ca/ZZeDbA
Less responsibilities 
More responsibilities 
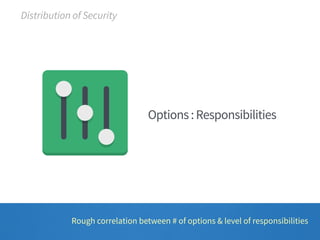
Distribution of Security
Options : Responsibilities 
Distribution of Security 
Rough correlation between # of options & level of responsibilities
RE:BOOT
Critical embargoed bug discovered in Xen, details at http://4mn.ca/1rcXTTN
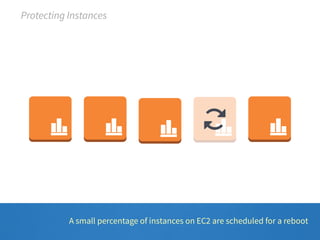
Protecting Instances 
A small percentage of instances on EC2 are scheduled for a reboot
Actions to Take 
For EC2 
Nothing for cloud-native architectures 
Manage availability for traditional architectures 
For RDS 
Nothing for Multi-AZ instances 
Standard maintenance window for single instances
POODLE
CVE-2014-3566 : Padding Oracle On Downgraded Legacy Encryption
Attack forces an older cipher choice, details at http://4mn.ca/1EYfBEA
For ELB 
Select a non-affected cipher suite (e.g., ELBSecurityPolicy-2014-10) 
For Web Servers 
Enable TLS_FALLBACK_SCSV 
Disable support for SSL 3.0* 
Disabling SSL 3.0 may cause compatibility issues 
Actions to Take
Shellshock
More info on bash at http://www.gnu.org/software/bash
(){}; attack 
10/10 vulnerability : widespread & easy to exploit
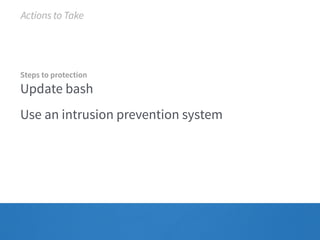
Actions to Take 
Steps to protection 
Update bash 
Use an intrusion prevention system
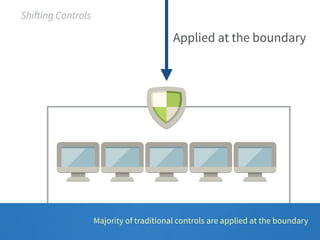
Applied at the boundary 
Majority of traditional controls are applied at the boundary 
Shifting Controls
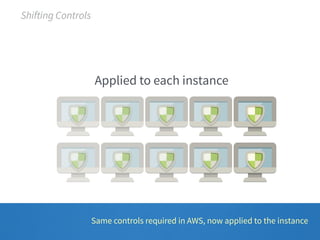
Applied to each instance 
Same controls required in AWS, now applied to the instance 
Shifting Controls
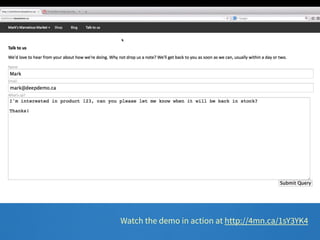
Watch the demo in action at http://4mn.ca/1sY3YK4
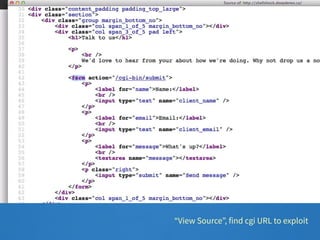
“View Source”, find cgi URL to exploit
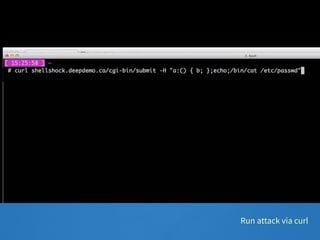
Run attack via curl
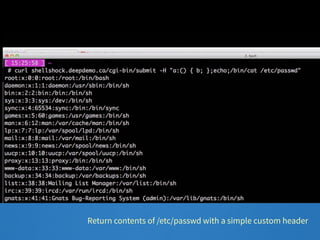
Return contents of /etc/passwd with a simple custom header
Add intrusion prevention controls to the instance
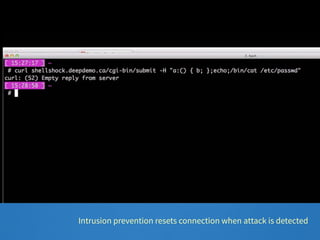
Intrusion prevention resets connection when attack is detected
Options : Responsibilities 
Where does you deployment fall on the scale?
Thank you! 
Learn more at 
testdrive.trendmicro.com 
Follow me on Twitter @marknca