Security on AWS, 2021 Edition Meetup
AWS User Groups of Florida –Virtual
April 8th, 2021
AWS User Groups of Florida – Updates
• Our fifth virtual MeetUp/nine months of virtual meetups
• Always open to ideas on how we can improve the content and format!
• Collaborate with us after the MeetUp!
• Future MeetUps – Presenters?Topics? Formats?
• Slideshare – Keep an eye on our MeetUp Page – we will post a link to the Slides
• Youtube – Keep an eye on our MeetUp Page – we will post a link to theVideo
• Slack – Keep the conversation going - http://aws-usergroup-florida.slack.com/
• Today’s MeetUp Format
• Feel free to ask questions/respond in the ChimeWindow throughout the session!
AWS User Groups of Florida – Coverage (sometime soon!)
• Doral: https://www.meetup.com/AWSUserGroupDoral
• Miami: https://www.meetup.com/Miami-AWS-Users-Group
• Miami Beach: https://www.meetup.com/aws-user-group-miami
• Fort Lauderdale: https://www.meetup.com/South-Florida-Amazon-Web-Services-Meetup
• Boca Raton: https://www.meetup.com/awsflorida
• Orlando: https://www.meetup.com/Orlando-AWS-Users-Group
• Tampa: https://www.meetup.com/Tampa-AWS-Users-Group
• Jacksonville: https://www.meetup.com/AWS-User-Groups-of-Florida-Jacksonville
Who am I?
• Who am I?
Who is CloudHesive?
• Professional Services
• Assessment (Current environment,
datacenter or cloud)
• Strategy (Getting to the future state)
• LandingZone (Pre-Migration)
• Migration (Environment-to-cloud,
Datacenter-to-cloud)
• Implementation (Point solutions)
• Support (Break/fix and ongoing
enhancement)
• DevOps Services
• Assessment
• Strategy
• Implementation (Point solutions)
• Management (Supporting infrastructure,
solutions or ongoing enhancement)
• Support (Break/fix and ongoing
enhancement)
• Managed Security Services (SecOps)
• Encryption as a Service (EaaS) –
encryption at rest/in flight
• End Point Security as a Service
• Threat Management
• SOC IIType 2Validated
• Next Generation Managed Services
(MSP)
• Leveraging our Professional, DevOps
and Managed Security Services
• Single payer billing
• Intelligent operations and
automation
• AWS Audited
• Cost Management
Topics
• Introduction
• End User Computing
• Ransomware Incident Response
• End User Computing Security Best Practices
• Modernizing Security Controls
• NIST Cybersecurity Framework
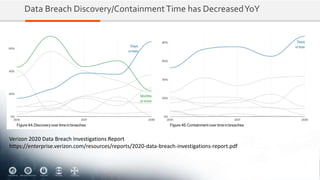
Data Breach Discovery/ContainmentTime has DecreasedYoY
Verizon 2020 Data Breach Investigations Report
https://enterprise.verizon.com/resources/reports/2020-data-breach-investigations-report.pdf
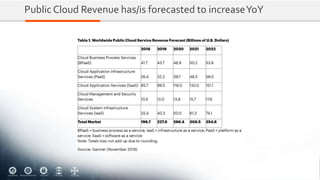
Public Cloud Revenue has/is forecasted to increaseYoY
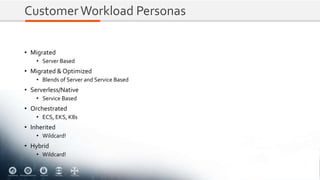
CustomerWorkload Personas
• Migrated
• Server Based
• Migrated & Optimized
• Blends of Server and Service Based
• Serverless/Native
• Service Based
• Orchestrated
• ECS, EKS, K8s
• Inherited
• Wildcard!
• Hybrid
• Wildcard!
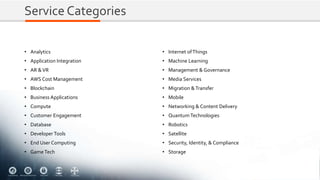
Service Categories
• Analytics
• Application Integration
• AR &VR
• AWS Cost Management
• Blockchain
• Business Applications
• Compute
• Customer Engagement
• Database
• Developer Tools
• End User Computing
• GameTech
• Internet ofThings
• Machine Learning
• Management & Governance
• Media Services
• Migration &Transfer
• Mobile
• Networking & Content Delivery
• QuantumTechnologies
• Robotics
• Satellite
• Security, Identity, & Compliance
• Storage
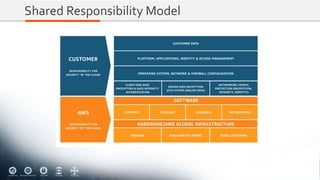
Shared Responsibility Model
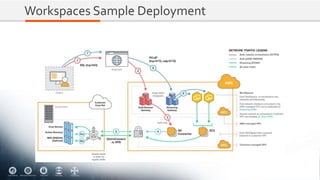
The Scenario
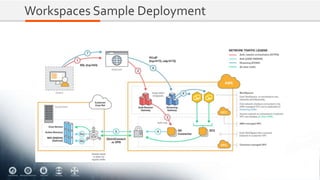
Workspaces Sample Deployment
What’s missing?
• Ingress Security Group toWorkspace
• Egress Security Group fromWorkspace to (Internet)
• Security Groups to/from other Services (AWS and On Premises)
• Security of the Workspace Environment
• Security of supporting servers (Active Directory)
• Security of other network-accessible resources (Web Servers)
• User Permissions (Non-Local Admin, Local Admin, Global Admin)
• Access of the Workspace (PKI Cert, PKI PIV, Network, MFA)
• The rest of the AWSAccount?The rest of the AWSAccount! (Services, APIs)
Workspaces Sample Deployment
What could go wrong?
• Ingress Security Group toWorkspace
• Egress Security Group fromWorkspace to (Internet)
• Security Groups to/from other Services (AWS and On Premises)
• Security of the Workspace Environment
• Security of supporting servers (Active Directory)
• Security of other network-accessible resources (Web Servers)
• User Permissions (Non-Local Admin, Local Admin, Global Admin)
• Access of the Workspace (PKI Cert, PKI PIV, Network, MFA)
• The rest of the AWSAccount?The rest of the AWSAccount! (Services, APIs)
The Approach
Overview
• Through the lens of the NIST Cybersecurity Framework we will look at frameworks developed
by, and services available onAWS.
• AWS services can either/both play a supporting role in your security posture, supporting both
non-AWS resources andAWS resources alike but secure configuration ofAWS resources can also
play a role in supporting your security posture.
• The NIST Cybersecurity Framework provides a policy framework of computer security guidance
for how private sector organizations in the United States can assess and improve their ability to
prevent, detect, and respond to cyber attacks.
NIST Cybersecurity Framework
• Identify
• Develop an organizational understanding to manage cybersecurity risk to systems, people, assets,
data, and capabilities.
• Protect
• Develop and implement appropriate safeguards to ensure delivery of critical services.
• Detect
• Develop and implement appropriate activities to identify the occurrence of a cybersecurity event.
• Respond
• Develop and implement appropriate activities to take action regarding a detected cybersecurity
incident.
• Recover
• Develop and implement appropriate activities to maintain plans for resilience and to restore any
capabilities or services that were impaired due to a cybersecurity incident.
CIS Controls & Benchmarks
• Controls
• Prescriptive Controls
• Benchmarks
• Prescriptive steps to apply controls to specific technologies
• AWS
• Workspaces
• Windows/Linux
• Other Services
CIS Benchmark End User Computing Example
CloudWorkload Lifecycle Management Framework
• Workload
• Architecture
• Monitoring
• Automation
• Processes
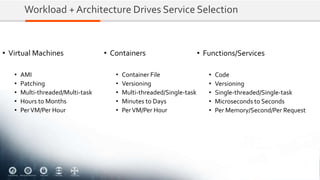
Workload + Architecture Drives Service Selection
• Virtual Machines
• AMI
• Patching
• Multi-threaded/Multi-task
• Hours to Months
• PerVM/Per Hour
• Functions/Services
• Code
• Versioning
• Single-threaded/Single-task
• Microseconds to Seconds
• Per Memory/Second/Per Request
• Containers
• Container File
• Versioning
• Multi-threaded/Single-task
• Minutes to Days
• PerVM/Per Hour
Integration
Automation + Processes Drives Lifecycle Management Selection
• Organizations
• Cross-AccountAsset Management + Governance
• ControlTower
• Account vending/default standardization
• Service Catalog
• Workload platform vending/default standardization
• CloudFormation
• IaC
• Ephemeral Compute + API Managed Data/Control Plane for PersistenceTiers
• Hands off/Lights out
Processes
• Patching
• Backup/RestoreTesting
• FailoverTesting (AZ)
• Credential Rotation/CredentialAudit
• Event ResponseTesting
• Incident ResponseTesting
• PerformanceTesting
• Performance/Cost Review
• Vulnerability/PenetrationTesting
Identify
Cloud Adoption Framework (CAF)
• Perspectives
• Business
• Value Realization
• People
• Roles & Readiness
• Governance
• Prioritization & Control
• Platform
• Applications & Infrastructure
• Security
• Risk & Compliance
• Operations
• Manage & Scale
CAF – Security Perspective
• Directive
• Account Ownership and contact information
• Change and asset management
• Least privilege access
• Preventive
• Identity and access
• Infrastructure protection
• Data protection
• Detective
• Logging and monitoring
• Asset inventory
• Change detection
• Responsive
• Vulnerabilities
• Privilege escalation
• DDoS attack
Well Architected Framework (WAF)
• General
• Event-Triggered
• Workload-Focused
• General Design Principals
• Pillars
• Design Principals
• Best Practices
• Lenses
WAF – Pillars
• Operational Excellence
• Security
• Reliability
• Performance Efficiency
• Cost Optimization
WAF – Lenses
• Financial Services Industry
• Analytics
• Machine Learning
• Internet ofThings (IOT)
• Serverless
• High Performance Computing (HPC)
WAF – General Design Principals
• Stop guessing your capacity needs
• Test systems at production scale
• Automate to make architectural experimentation easier
• Allow for evolutionary architectures
• Drive architectures using data
• Improve through game days
WAF – Game Days
• Prepare
• Is the process/are the processes to be tested during the game day well defined? Is access in place? Has
training been performed?
• Define
• Workload, Personnel, Scenario, Environment, Schedule
• Execute
• Start, Middle, End
• Analyze
• Debrief, Examine, Document, Root Cause Analysis (RCA), Correction of Error (CoE)
WAF – Security Pillar
• Design Principles
• Implement a strong identity foundation
• Enable traceability
• Apply security at all layers
• Automate security best practices
• Protect data in transit and at rest
• Keep people away from data
• Prepare for security events
• Best Practices
• Identity and Access Management
• Detection
• Infrastructure Protection
• Data Protection
• Incident Response
Identify
• Audit Manager
• Cost Management Services (Individual Services)
• Certificate Manager (Public + Private)
• Firewall Manager (WAF + Security Groups)
• Directory Service + Identity and Access Management (+ Services with their own Policies)
• AccessAdvisor,Access Analyzer,Organization Activity
• Inspector
• Key Management Service + Secrets Manager
• Macie
• Premium Support +Trusted Advisor + Personal Health Dashboard
• Systems Manager
• Security Hub + Config + Config Rules
• Tags
Identify – Organizations
• Tag policies
• Artifact
• Backup
• CloudFormation StackSets
• CloudTrail
• Config
• Directory Service
• Firewall Manager
• Resource Access Manager
• Service Catalog
• Single Sign-On
• Systems Manager
Protect/Detect
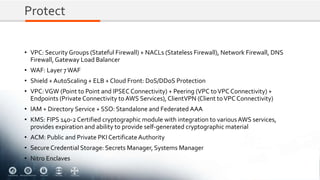
Protect
• VPC: Security Groups (Stateful Firewall) + NACLs (Stateless Firewall), Network Firewall, DNS
Firewall,Gateway Load Balancer
• WAF: Layer 7WAF
• Shield + AutoScaling + ELB + Cloud Front: DoS/DDoS Protection
• VPC:VGW (Point to Point and IPSECConnectivity) + Peering (VPC toVPC Connectivity) +
Endpoints (Private Connectivity to AWS Services), ClientVPN (Client toVPC Connectivity)
• IAM + Directory Service + SSO: Standalone and Federated AAA
• KMS: FIPS 140-2 Certified cryptographic module with integration to various AWS services,
provides expiration and ability to provide self-generated cryptographic material
• ACM: Public and Private PKI Certificate Authority
• Secure Credential Storage: Secrets Manager, Systems Manager
• Nitro Enclaves
Protect
• AWS Auto Scaling: EC2, Dynamo,Aurora Autoscaling
• Code Commit/ECS (Image Scanning)/Signer: Secure Application and Artifact Repository +
dedicated account
• Code Deploy/Systems Manager: “Hands off” OS and configuration management + application
deployment
• EC2: Systems Manager (OS and above patching + auditing), Amazon Linux 2 Live Patching
• AWS Backup: EC2, RDS, EFS, Dynamo Backups + dedicated account
• Workspaces: Secure Bastion
• CloudFormation + OpsWorks + Elastic Beanstalk: “Hands off” infrastructure management
• S3/Glacier: File based storage with AAA, versioning, secure delete + policy based retention
• Host Based Security
Detect
Detect
• Guard Duty
• Config: Point in time snapshots of configuration items, Exportable as JSON to
idempotent storage
• VPC: Flow Logs (NetFlow) + Port Mirroring
• CloudWatch Logs: OS and above log management
• CloudTrail: AuditTrail, Exportable as JSON to idempotent storage
• Cloudfront, ALB andWAF: All log (CloudFront and ALB in S3,WAF in Kinesis)
• S3/Glacier: File based storage with AAA, versioning, secure delete + policy based
retention + dedicated account
Respond/Recover
Respond
• Detective
• Disk Snapshots
• Don’t forget to remove from retention policy
• Automated withThreatResponse,GRR
• Memory Snapshots
• Automated withThreatResponse,GRR,Volatility, Rekall
• Logs
• Don’t forget to remove from retention policy
• Query and Correlate with Athena
• Measure
Recover
• Block Access
• Revert to Known Good State
• Identify/Correct Root Cause
• Rotate Credentials (people and things)
• Measure
Conclusion
• Iterate introduction of your security controls – some in the short term is better than none in the
long term.
• Detective Controls are just as important as Preventative Controls, they play a significant
response in incident detection and response.
• Whether your workload is onAWS or not,AWS services can be used to supplement your controls.
• There is no lack of frameworks – pick and choose from them to make a framework that works
best for your organization’s needs.
Q&A
Contact Us
• Partner Solutions Finder
• https://aws.amazon.com/partners/find/partnerdetails/?n=CloudHesive&id=001E000000qK5f6IAC
• E-Mail
• sales@cloudhesive.com
• URL
• https://cloudhesive.com
• Phone
• United States: 800-860-2040 x1 (Miami, Florida, US & Norfolk,Virginia, US)
• Argentina: +54 (11) 51737475 x1 (Buenos Aires,AR & Santiago,CL)
• United Kingdom: +44 (20) 37955127 x1
• Australia: +61 (2) 80742932 x1