Downloaded 129 times

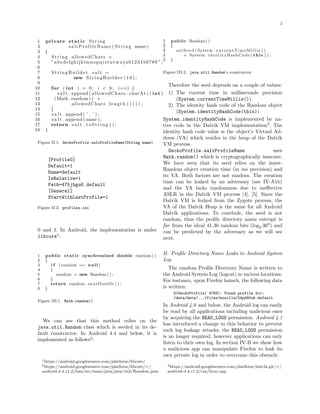
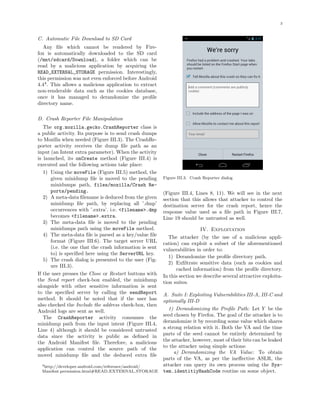
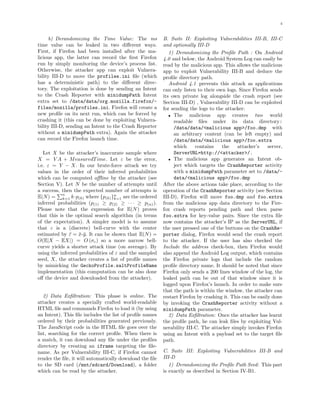
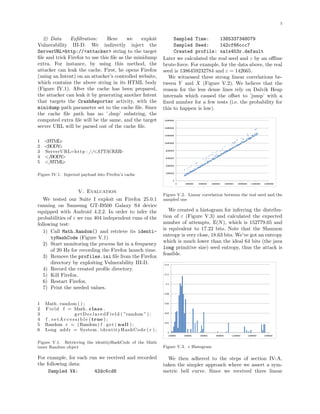
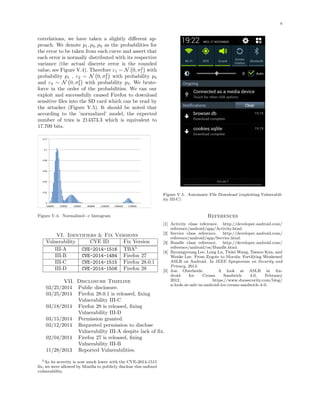

The document details newly identified vulnerabilities in the Firefox Android application that allow exploitation by malicious apps to access sensitive user data. It discusses the weak randomization of profile directory names and the leakage of such data through Android system logs and automatic file downloads. Recommendations for exploitation are provided, outlining the steps by which an attacker can derandomize the profile directory path and exfiltrate data from it.


