Master Kubernetes Security Faster with Reliable KCSA Exam Dumps
1.
Linux Foundation
KCSA
Kubernetes andCloud Native Security Associate (KCSA)
QUESTION & ANSWERS
Limited Time: 20% Off KCSA Packages Using Code: WELCOME20
Click Here to Download: https://www.dumps4less.com/KCSA-dumps-pdf.html
2.
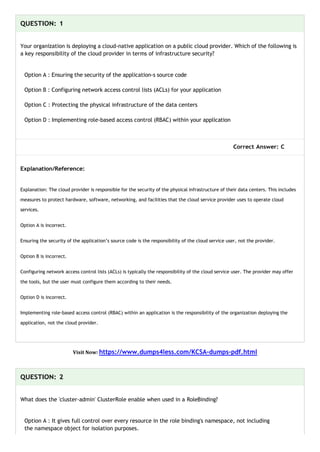
QUESTION: 1
Your organizationis deploying a cloud-native application on a public cloud provider. Which of the following is
a key responsibility of the cloud provider in terms of infrastructure security?
Option A : Ensuring the security of the application-s source code
Option B : Configuring network access control lists (ACLs) for your application
Option C : Protecting the physical infrastructure of the data centers
Option D : Implementing role-based access control (RBAC) within your application
Correct Answer: C
Explanation/Reference:
Explanation: The cloud provider is responsible for the security of the physical infrastructure of their data centers. This includes
measures to protect hardware, software, networking, and facilities that the cloud service provider uses to operate cloud
services.
Option A is incorrect.
Ensuring the security of the application’s source code is the responsibility of the cloud service user, not the provider.
Option B is incorrect.
Configuring network access control lists (ACLs) is typically the responsibility of the cloud service user. The provider may offer
the tools, but the user must configure them according to their needs.
Option D is incorrect.
Implementing role-based access control (RBAC) within an application is the responsibility of the organization deploying the
application, not the cloud provider.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 2
What does the 'cluster-admin' ClusterRole enable when used in a RoleBinding?
Option A : It gives full control over every resource in the role binding's namespace, not including
the namespace object for isolation purposes.
3.
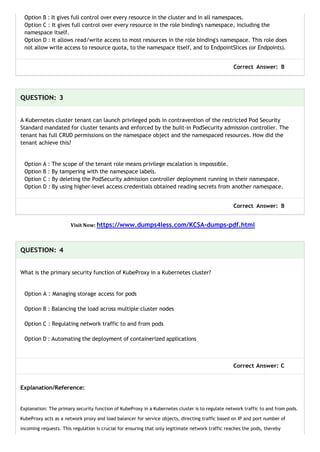
Option B :It gives full control over every resource in the cluster and in all namespaces.
Option C : It gives full control over every resource in the role binding's namespace, including the
namespace itself.
Option D : It allows read/write access to most resources in the role binding's namespace. This role does
not allow write access to resource quota, to the namespace itself, and to EndpointSlices (or Endpoints).
Correct Answer: B
QUESTION: 3
A Kubernetes cluster tenant can launch privileged pods in contravention of the restricted Pod Security
Standard mandated for cluster tenants and enforced by the built-in PodSecurity admission controller. The
tenant has full CRUD permissions on the namespace object and the namespaced resources. How did the
tenant achieve this?
Option A : The scope of the tenant role means privilege escalation is impossible.
Option B : By tampering with the namespace labels.
Option C : By deleting the PodSecurity admission controller deployment running in their namespace.
Option D : By using higher-level access credentials obtained reading secrets from another namespace.
Correct Answer: B
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
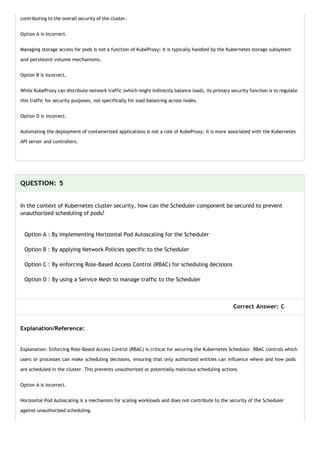
QUESTION: 4
What is the primary security function of KubeProxy in a Kubernetes cluster?
Option A : Managing storage access for pods
Option B : Balancing the load across multiple cluster nodes
Option C : Regulating network traffic to and from pods
Option D : Automating the deployment of containerized applications
Correct Answer: C
Explanation/Reference:
Explanation: The primary security function of KubeProxy in a Kubernetes cluster is to regulate network traffic to and from pods.
KubeProxy acts as a network proxy and load balancer for service objects, directing traffic based on IP and port number of
incoming requests. This regulation is crucial for ensuring that only legitimate network traffic reaches the pods, thereby
4.
contributing to theoverall security of the cluster.
Option A is incorrect.
Managing storage access for pods is not a function of KubeProxy; it is typically handled by the Kubernetes storage subsystem
and persistent volume mechanisms.
Option B is incorrect.
While KubeProxy can distribute network traffic (which might indirectly balance load), its primary security function is to regulate
this traffic for security purposes, not specifically for load balancing across nodes.
Option D is incorrect.
Automating the deployment of containerized applications is not a role of KubeProxy; it is more associated with the Kubernetes
API server and controllers.
QUESTION: 5
In the context of Kubernetes cluster security, how can the Scheduler component be secured to prevent
unauthorized scheduling of pods?
Option A : By implementing Horizontal Pod Autoscaling for the Scheduler
Option B : By applying Network Policies specific to the Scheduler
Option C : By enforcing Role-Based Access Control (RBAC) for scheduling decisions
Option D : By using a Service Mesh to manage traffic to the Scheduler
Correct Answer: C
Explanation/Reference:
Explanation: Enforcing Role-Based Access Control (RBAC) is critical for securing the Kubernetes Scheduler. RBAC controls which
users or processes can make scheduling decisions, ensuring that only authorized entities can influence where and how pods
are scheduled in the cluster. This prevents unauthorized or potentially malicious scheduling actions.
Option A is incorrect.
Horizontal Pod Autoscaling is a mechanism for scaling workloads and does not contribute to the security of the Scheduler
against unauthorized scheduling.
5.
Option B isincorrect.
Applying Network Policies is important for controlling pod-to-pod communication but does not directly secure the Scheduler
against unauthorized scheduling decisions.
Option D is incorrect.
Using a Service Mesh can manage and secure traffic within a cluster, but it does not directly enforce security policies on the
Scheduler’s scheduling decisions.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 6
In Kubernetes, what is a key security practice for pods to ensure that they only communicate with authorized
services or components within the cluster?
Option A : Configuring the Horizontal Pod Autoscaler for each pod
Option B : Implementing Pod Security Policies
Option C : Enabling Readiness and Liveness Probes for each pod
Option D : Applying Network Policies to pods
Correct Answer: D
Explanation/Reference:
Explanation: Applying Network Policies to pods in Kubernetes is a key security practice to control and restrict which network
connections are allowed to and from the pods. This ensures that pods only communicate with authorized services or
components, thereby preventing potential security breaches through unauthorized network access.
Option A is incorrect.
Configuring the Horizontal Pod Autoscaler is important for scaling pods based on load but does not contribute to network
security or restrict communication with unauthorized services.
Option B is incorrect.
Implementing Pod Security Policies is crucial for defining security-related conditions pods must meet to run, but it does not
directly control network communication between pods.
Option C is incorrect.
6.
Enabling Readiness andLiveness Probes ensures the health and availability of pods but does not govern their network
communication with other services.
QUESTION: 7
What is the primary security advantage of using client certificate authentication for access to the Kubernetes
API server?
Option A : To accelerate the deployment of applications via the Kubernetes API
Option B : To optimize the management of Kubernetes resource quotas
Option C : To ensure a secure method of authentication that reduces the risk of credential theft or misuse
Option D : To facilitate automated scaling of resources based on access patterns
Correct Answer: C
Explanation/Reference:
Explanation: The primary security advantage of using client certificate authentication for access to the Kubernetes API server is
to ensure a secure method of authentication that reduces the risk of credential theft or misuse. Certificates offer a more robust
and secure form of authentication compared to basic username and password methods. They are less susceptible to common
attack vectors like phishing, and their use helps in mitigating risks associated with credential exposure or theft. This method
ensures a higher level of security for access to the Kubernetes cluster.
Option A is incorrect.
While accelerating application deployment is an operational benefit, it is not the primary security advantage of using client
certificate authentication.
Option B is incorrect.
Optimizing the management of resource quotas is not related to the method of authentication used for API server access.
Option D is incorrect.
Automated scaling of resources based on access patterns is an operational feature, not a direct benefit of using client
certificate authentication.
7.
QUESTION: 8
In Kubernetes,why is implementing Role-Based Access Control (RBAC) essential for securing access to
sensitive data?
Option A : To optimize resource allocation based on data access requirements
Option B : To facilitate automated scaling of resources accessing the data
Option C : To ensure that only authorized users and applications can access the sensitive data
Option D : To enhance the performance of applications accessing the sensitive data
Correct Answer: C
Explanation/Reference:
Explanation: Implementing Role-Based Access Control (RBAC) in Kubernetes is essential for securing access to sensitive data
because it ensures that only authorized users and applications can access this data. RBAC allows administrators to define roles
with specific permissions and then assign these roles to users, groups, or service accounts. This access control mechanism is
crucial for enforcing the principle of least privilege, where entities are only granted the access necessary to perform their
functions, thereby reducing the risk of unauthorized data exposure or breaches.
Option A is incorrect.
Optimizing resource allocation is important for operational efficiency but does not directly relate to securing access to sensitive
data, which is the primary role of RBAC.
Option B is incorrect.
Automated scaling of resources is an operational feature of Kubernetes and is not specifically related to the security function of
RBAC in protecting sensitive data.
Option D is incorrect.
Enhancing the performance of applications accessing sensitive data is a benefit, but the primary reason for RBAC is to control
and secure access to sensitive data.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 9
What is the primary security advantage of using client certificate authentication for Kubernetes API server
8.
access?
Option A :To enable rapid deployment of Kubernetes resources
Option B : To provide a secure method of authentication that minimizes the risk of credential theft
Option C : To optimize the network traffic flow within the Kubernetes cluster
Option D : To facilitate the integration of Kubernetes with cloud-based storage services
Correct Answer: B
Explanation/Reference:
Explanation: The primary security advantage of using client certificate authentication for Kubernetes API server access is to
provide a secure method of authentication that minimizes the risk of credential theft. Client certificate authentication uses
digital certificates rather than conventional passwords, offering a stronger and more secure form of authentication. Certificates
are less susceptible to common attacks such as phishing, significantly reducing the risk of unauthorized access to the
Kubernetes API server.
Option A is incorrect.
While rapid deployment of resources is important, it is not related to the security advantage of client certificate authentication,
which focuses on minimizing credential theft.
Option C is incorrect.
Optimizing network traffic flow within the Kubernetes cluster is not directly related to the method of authentication. Client
certificate authentication’s primary purpose is to enhance security.
Option D is incorrect.
Facilitating integration with cloud-based storage services is not a direct benefit of using client certificate authentication for the
Kubernetes API server, which is primarily about secure authentication.
QUESTION: 10
Why is it important to regularly review and analyze Kubernetes audit logs?
Option A : To improve the performance of applications running in the cluster
Option B : To ensure high availability of services within the cluster
9.
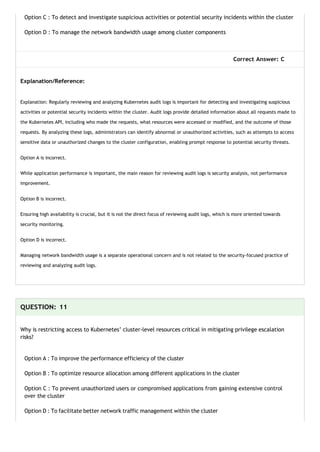
Option C :To detect and investigate suspicious activities or potential security incidents within the cluster
Option D : To manage the network bandwidth usage among cluster components
Correct Answer: C
Explanation/Reference:
Explanation: Regularly reviewing and analyzing Kubernetes audit logs is important for detecting and investigating suspicious
activities or potential security incidents within the cluster. Audit logs provide detailed information about all requests made to
the Kubernetes API, including who made the requests, what resources were accessed or modified, and the outcome of those
requests. By analyzing these logs, administrators can identify abnormal or unauthorized activities, such as attempts to access
sensitive data or unauthorized changes to the cluster configuration, enabling prompt response to potential security threats.
Option A is incorrect.
While application performance is important, the main reason for reviewing audit logs is security analysis, not performance
improvement.
Option B is incorrect.
Ensuring high availability is crucial, but it is not the direct focus of reviewing audit logs, which is more oriented towards
security monitoring.
Option D is incorrect.
Managing network bandwidth usage is a separate operational concern and is not related to the security-focused practice of
reviewing and analyzing audit logs.
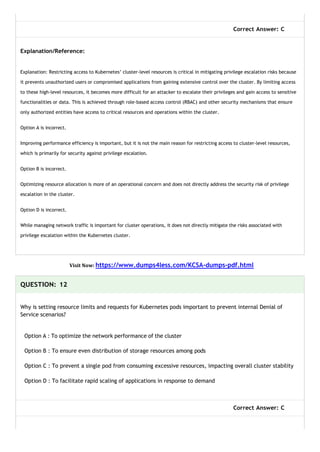
QUESTION: 11
Why is restricting access to Kubernetes’ cluster-level resources critical in mitigating privilege escalation
risks?
Option A : To improve the performance efficiency of the cluster
Option B : To optimize resource allocation among different applications in the cluster
Option C : To prevent unauthorized users or compromised applications from gaining extensive control
over the cluster
Option D : To facilitate better network traffic management within the cluster
10.
Correct Answer: C
Explanation/Reference:
Explanation:Restricting access to Kubernetes’ cluster-level resources is critical in mitigating privilege escalation risks because
it prevents unauthorized users or compromised applications from gaining extensive control over the cluster. By limiting access
to these high-level resources, it becomes more difficult for an attacker to escalate their privileges and gain access to sensitive
functionalities or data. This is achieved through role-based access control (RBAC) and other security mechanisms that ensure
only authorized entities have access to critical resources and operations within the cluster.
Option A is incorrect.
Improving performance efficiency is important, but it is not the main reason for restricting access to cluster-level resources,
which is primarily for security against privilege escalation.
Option B is incorrect.
Optimizing resource allocation is more of an operational concern and does not directly address the security risk of privilege
escalation in the cluster.
Option D is incorrect.
While managing network traffic is important for cluster operations, it does not directly mitigate the risks associated with
privilege escalation within the Kubernetes cluster.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
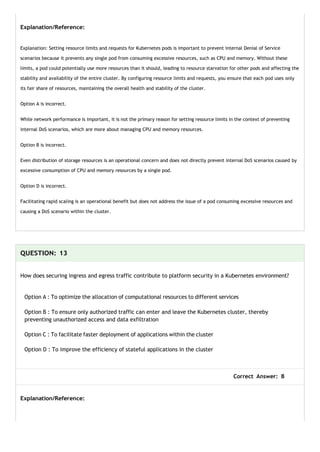
QUESTION: 12
Why is setting resource limits and requests for Kubernetes pods important to prevent internal Denial of
Service scenarios?
Option A : To optimize the network performance of the cluster
Option B : To ensure even distribution of storage resources among pods
Option C : To prevent a single pod from consuming excessive resources, impacting overall cluster stability
Option D : To facilitate rapid scaling of applications in response to demand
Correct Answer: C
11.
Explanation/Reference:
Explanation: Setting resourcelimits and requests for Kubernetes pods is important to prevent internal Denial of Service
scenarios because it prevents any single pod from consuming excessive resources, such as CPU and memory. Without these
limits, a pod could potentially use more resources than it should, leading to resource starvation for other pods and affecting the
stability and availability of the entire cluster. By configuring resource limits and requests, you ensure that each pod uses only
its fair share of resources, maintaining the overall health and stability of the cluster.
Option A is incorrect.
While network performance is important, it is not the primary reason for setting resource limits in the context of preventing
internal DoS scenarios, which are more about managing CPU and memory resources.
Option B is incorrect.
Even distribution of storage resources is an operational concern and does not directly prevent internal DoS scenarios caused by
excessive consumption of CPU and memory resources by a single pod.
Option D is incorrect.
Facilitating rapid scaling is an operational benefit but does not address the issue of a pod consuming excessive resources and
causing a DoS scenario within the cluster.
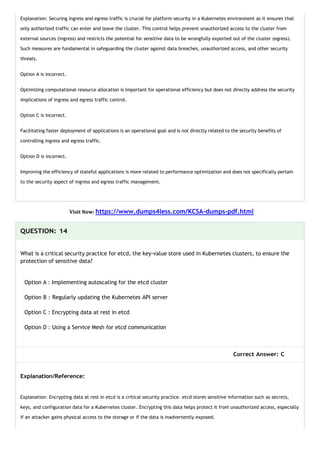
QUESTION: 13
How does securing ingress and egress traffic contribute to platform security in a Kubernetes environment?
Option A : To optimize the allocation of computational resources to different services
Option B : To ensure only authorized traffic can enter and leave the Kubernetes cluster, thereby
preventing unauthorized access and data exfiltration
Option C : To facilitate faster deployment of applications within the cluster
Option D : To improve the efficiency of stateful applications in the cluster
Correct Answer: B
Explanation/Reference:
12.
Explanation: Securing ingressand egress traffic is crucial for platform security in a Kubernetes environment as it ensures that
only authorized traffic can enter and leave the cluster. This control helps prevent unauthorized access to the cluster from
external sources (ingress) and restricts the potential for sensitive data to be wrongfully exported out of the cluster (egress).
Such measures are fundamental in safeguarding the cluster against data breaches, unauthorized access, and other security
threats.
Option A is incorrect.
Optimizing computational resource allocation is important for operational efficiency but does not directly address the security
implications of ingress and egress traffic control.
Option C is incorrect.
Facilitating faster deployment of applications is an operational goal and is not directly related to the security benefits of
controlling ingress and egress traffic.
Option D is incorrect.
Improving the efficiency of stateful applications is more related to performance optimization and does not specifically pertain
to the security aspect of ingress and egress traffic management.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 14
What is a critical security practice for etcd, the key-value store used in Kubernetes clusters, to ensure the
protection of sensitive data?
Option A : Implementing autoscaling for the etcd cluster
Option B : Regularly updating the Kubernetes API server
Option C : Encrypting data at rest in etcd
Option D : Using a Service Mesh for etcd communication
Correct Answer: C
Explanation/Reference:
Explanation: Encrypting data at rest in etcd is a critical security practice. etcd stores sensitive information such as secrets,
keys, and configuration data for a Kubernetes cluster. Encrypting this data helps protect it from unauthorized access, especially
if an attacker gains physical access to the storage or if the data is inadvertently exposed.
13.
Option A isincorrect.
While autoscaling is important for performance and availability, it does not directly address the security of sensitive data
stored in etcd.
Option B is incorrect.
Regularly updating the Kubernetes API server is crucial for overall cluster security, but it does not specifically secure the data
stored in etcd.
Option D is incorrect.
Using a Service Mesh can help manage and secure communication between services, but it is not a direct method for securing
the data stored in etcd.
QUESTION: 15
By default, in a Kubeadm cluster, which authentication methods are enabled?
Option A : OIDC, Bootstrap tokens, and Service Account Tokens
Option B : X509 Client Certs, OIDC, and Service Account Tokens
Option C : X509 Client Certs, Bootstrap Tokens, and Service Account Tokens
Option D : X509 Client Certs, Webhook Authentication, and Service Account Tokens
Correct Answer: C
QUESTION: 16
Why is it important to have a robust PKI and certificate management strategy in Kubernetes?
Option A : To enhance the deployment speed of Kubernetes pods
Option B : To ensure efficient resource allocation within the Kubernetes cluster
Option C : To prevent unauthorized access and ensure encrypted communication between cluster
components
Option D : To facilitate seamless integration with external monitoring tools
Correct Answer: C
14.
Explanation/Reference:
Explanation: Having arobust PKI and certificate management strategy in Kubernetes is important to prevent unauthorized
access and ensure encrypted communication between cluster components. Proper management of PKI and certificates ensures
that each component in the cluster can securely authenticate the identity of other components and establish encrypted
channels for data transmission. This is vital for protecting sensitive data within the cluster and safeguarding the Kubernetes
environment from potential security breaches and eavesdropping.
Option A is incorrect.
Enhancing the deployment speed of pods is a performance-related aspect and does not directly address the security benefits
provided by a robust PKI and certificate management strategy.
Option B is incorrect.
Ensuring efficient resource allocation is important for operational efficiency but does not directly relate to the security
implications of PKI and certificate management in Kubernetes.
Option D is incorrect.
Facilitating integration with external monitoring tools is beneficial for observability but is not the primary reason for
emphasizing a robust PKI and certificate management strategy in Kubernetes security.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 17
What is the primary purpose of configuring audit logs in a Kubernetes environment?
Option A : To enhance the load balancing efficiency across different nodes
Option B : To track and record actions taken on the Kubernetes API for security monitoring and analysis
Option C : To automatically adjust pod scaling based on logged events
Option D : To optimize the allocation of storage resources in the cluster
Correct Answer: B
Explanation/Reference:
Explanation: The primary purpose of configuring audit logs in a Kubernetes environment is to track and record actions taken on
15.
the Kubernetes API.These logs provide a historical record of operations, such as who made which requests, what was
requested, and whether the requests were successful. This is crucial for security monitoring and analysis as it allows
administrators to review and analyze activities within the cluster, identify potential security breaches or unauthorized
activities, and take appropriate actions to enhance security and compliance.
Option A is incorrect.
While load balancing is important in Kubernetes, audit logs are not related to load balancing efficiency but are focused on
tracking and recording API activities for security purposes.
Option C is incorrect.
Automatic pod scaling is managed by Kubernetes controllers and metrics, not directly influenced by audit logs.
Option D is incorrect.
Optimizing the allocation of storage resources is an operational concern and is not the primary goal of audit logging, which is
aimed at security monitoring and analysis.
QUESTION: 18
When assessing the security responsibilities in a cloud-native environment, which of these tasks is primarily
the responsibility of the cloud provider under the shared responsibility model?
Option A : Configuring firewalls within the virtual network
Option B : Patching the guest operating systems of virtual machines
Option C : Ensuring physical security of data center facilities
Option D : Managing the encryption keys for data at rest
Correct Answer: C
Explanation/Reference:
Explanation: In the shared responsibility model, the cloud provider is primarily responsible for the physical security of the data
center facilities. This includes safeguarding the infrastructure against physical threats and ensuring the physical integrity and
availability of the hardware and facilities where the cloud services operate.
Option A is incorrect.
16.
Configuring firewalls withinthe virtual network is typically the responsibility of the cloud service user, as it involves the security
configuration of the cloud services being used.
Option B is incorrect.
Patching the guest operating systems of virtual machines is generally the responsibility of the cloud service user, as it falls
under the management of the software environment on the cloud platform.
Option D is incorrect.
Managing the encryption keys for data at rest, especially when using customer-managed keys, is usually the responsibility of
the cloud service user, not the cloud provider.
QUESTION: 19
In Kubernetes, what is a key security practice for container networking to prevent unauthorized access and
network attacks?
Option A : Regularly updating container runtime environments
Option B : Implementing Network Policies to control pod-to-pod communication
Option C : Using Horizontal Pod Autoscaling for network traffic management
Option D : Encrypting data stored within containers
Correct Answer: B
Explanation/Reference:
Explanation: Implementing Network Policies in Kubernetes is a crucial security practice for container networking. These policies
allow administrators to define rules that govern how pods can communicate with each other and with other network endpoints.
By controlling pod-to-pod communication, Network Policies help prevent unauthorized access and potential network attacks,
such as traffic snooping or denial-of-service attacks.
Option A is incorrect.
Regularly updating container runtime environments is important for overall container security, but it doesn’t specifically
address network communication control between pods.
Option C is incorrect.
17.
Using Horizontal PodAutoscaling helps manage the scaling of pods based on traffic, but it doesn’t provide direct security
measures for pod-to-pod communication.
Option D is incorrect.
Encrypting data stored within containers is a critical security practice but does not relate directly to securing container
networking or controlling pod-to-pod communication.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 20
Why is implementing centralized logging in a Kubernetes environment considered critical for security
observability?
Option A : To enhance data processing speed across microservices
Option B : To manage the distribution of traffic among services
Option C : To enable comprehensive tracking and analysis of security incidents across the cluster
Option D : To optimize resource allocation based on log analysis
Correct Answer: C
Explanation/Reference:
Explanation: Implementing centralized logging in a Kubernetes environment is critical for security observability as it enables
comprehensive tracking and analysis of security incidents across the cluster. Centralized logging provides a unified view of logs
from all components, making it easier to detect, investigate, and respond to security incidents. This holistic view is essential for
understanding the context of security events, identifying patterns of malicious activity, and ensuring that potential threats are
promptly addressed.
Option A is incorrect.
While enhancing data processing speed is important, it is not the primary reason for implementing centralized logging in the
context of security observability.
Option B is incorrect.
Managing traffic distribution is more related to network performance and load balancing, and does not directly pertain to the
role of centralized logging in security observability.
Option D is incorrect.
18.
Optimizing resource allocationbased on log analysis is an operational aspect but does not capture the essence of why
centralized logging is critical for security observability in Kubernetes.
QUESTION: 21
In a Kubernetes environment, which measure is most effective in protecting sensitive data processed by
applications from exposure?
Option A : Configuring liveness and readiness probes
Option B : Encrypting data in transit and at rest
Option C : Limiting resource quotas for pods
Option D : Implementing automated backup solutions
Correct Answer: B
Explanation/Reference:
Explanation: Encrypting data in transit and at rest is a fundamental security measure in Kubernetes environments to protect
sensitive data processed by applications. Encryption ensures that even if data is intercepted or accessed by unauthorized
entities, it remains unreadable and secure.
Option A is incorrect.
Configuring liveness and readiness probes is important for maintaining the health and availability of applications but does not
contribute to the protection of sensitive data.
Option C is incorrect.
Limiting resource quotas for pods is a practice for managing resources in Kubernetes but does not protect sensitive data from
exposure.
Option D is incorrect.
Implementing automated backup solutions is crucial for data recovery and resilience but does not directly protect data from
exposure while it is being processed by applications.
19.
QUESTION: 22
What isGrafana?
Option A : A cloud-native distributed tracing system for monitoring microservices architectures.
Option B : A container orchestration platform for managing and scaling applications.
Option C : A platform for monitoring and visualizing time-series data.
Option D : A cloud-native security tool for scanning and detecting vulnerabilities in Kubernetes clusters.
Correct Answer: C
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 23
In the context of Kubernetes, why is adherence to compliance frameworks like ISO 27001 important?
Option A : To enhance the overall performance of the Kubernetes cluster
Option B : To ensure that Kubernetes deployments align with international security standards and best
practices
Option C : To streamline the deployment process of applications in Kubernetes
Option D : To optimize the resource allocation within the Kubernetes environment
Correct Answer: B
Explanation/Reference:
Explanation: Adherence to compliance frameworks like ISO 27001 in the context of Kubernetes is important to ensure that
deployments align with international security standards and best practices. These frameworks provide a set of guidelines and
requirements for establishing, implementing, maintaining, and continually improving an information security management
system (ISMS). Compliance helps ensure that Kubernetes environments are secure, resilient, and protect sensitive data,
thereby reducing the risk of security breaches and enhancing trust among stakeholders.
Option A is incorrect.
Enhancing the overall performance of the Kubernetes cluster, while important, is not directly related to compliance with
security standards.
Option C is incorrect.
20.
Streamlining the deploymentprocess is an operational concern and does not specifically pertain to the security and compliance
aspects covered by frameworks like ISO 27001.
Option D is incorrect.
Optimizing resource allocation is more related to operational efficiency and is not the primary focus of compliance frameworks.
QUESTION: 24
In the context of cloud-native application deployment, what is the primary purpose of implementing a
container image scanning solution in your CI/CD pipeline?
Option A : To optimize the size and performance of container images
Option B : To ensure high availability of container images in the repository
Option C : To detect and remediate vulnerabilities within container images
Option D : To automate the deployment process of container images
Correct Answer: C
Explanation/Reference:
Explanation: Implementing a container image scanning solution in the CI/CD pipeline is primarily aimed at detecting and
remediating vulnerabilities within container images. This ensures that the images being deployed into the production
environment are free from known security issues, thereby enhancing the overall security posture of the application.
Option A is incorrect.
Optimizing the size and performance of container images is a goal of image optimization techniques, not specifically related to
security scanning.
Option B is incorrect.
Ensuring high availability of container images in the repository is more related to infrastructure and repository management
than to the security scanning of images.
Option D is incorrect.
While container image scanning can be part of an automated deployment process, its primary purpose is not automation but
the detection and remediation of security vulnerabilities.
21.
QUESTION: 25
Given astandard Kubernetes cluster architecture comprising a single control plane node (hosting both etcd
and the control plane as Pods) and three worker nodes, which of the following data flows crosses a trust
boundary?
Option A : From kubelet to Container Runtime
Option B : From kubelet to API Server
Option C : From kubelet to Controller Manager
Option D : From API Server to Container Runtime
Correct Answer: B
QUESTION: 26
Why is role-based access control (RBAC) important in managing access to sensitive data in Kubernetes?
Option A : To optimize the allocation of resources among different applications accessing the data
Option B : To ensure that only authorized users or processes have access to the sensitive data
Option C : To enhance the speed of data retrieval from storage resources
Option D : To facilitate load balancing and efficient traffic management to data storage services
Correct Answer: B
Explanation/Reference:
Explanation: Role-based access control (RBAC) is important in managing access to sensitive data in Kubernetes because it
ensures that only authorized users or processes can access this data. RBAC allows administrators to define roles with specific
permissions and assign them to users, groups, or service accounts. By controlling who can access sensitive data based on their
roles, RBAC plays a crucial role in protecting the data from unauthorized access, thereby maintaining data confidentiality and
security within the Kubernetes environment.
Option A is incorrect.
While resource allocation optimization is important, it is not the primary role of RBAC, which is focused on controlling access to
sensitive data.
22.
Option C isincorrect.
Enhancing the speed of data retrieval is a performance concern and is not directly related to RBAC’s role in managing access to
sensitive data.
Option D is incorrect.
Facilitating load balancing and efficient traffic management is not the primary purpose of RBAC in the context of access to
sensitive data.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 27
Which step would give an attacker a foothold in a cluster but no long-term persistence?
Option A : Modify Kubernetes objects stored within etcd.
Option B : Modify file on host filesystem.
Option C : Starting a process in a running container.
Option D : Create restarting container on host using Docker.
Correct Answer: C
QUESTION: 28
Why is network segmentation using Network Policies important in a Kubernetes cluster?
Option A : To optimize the network performance for high-traffic applications
Option B : To control and limit the network communication between different pods for security purposes
Option C : To manage the distribution of external traffic to different services
Option D : To automate the process of scaling network resources based on demand
Correct Answer: B
Explanation/Reference:
Explanation: Network segmentation using Network Policies in a Kubernetes cluster is important to control and limit the network
communication between different pods for security purposes. Network Policies allow administrators to define fine-grained rules
23.
for how podscan communicate with each other and with other network endpoints. This is vital for security, as it helps in
creating a controlled network environment where only authorized network connections are allowed, thereby reducing the risk
of lateral movement in case of a security breach and preventing unauthorized access to sensitive pods or services.
Option A is incorrect.
While optimizing network performance is important, the primary purpose of Network Policies is to enhance security through
controlled communication, not performance optimization.
Option C is incorrect.
Managing the distribution of external traffic to services is more related to Ingress controllers and load balancers, not the
primary function of Network Policies, which focus on pod-to-pod communication within the cluster.
Option D is incorrect.
Automating the scaling of network resources is a concern of resource management, not the primary security objective of
Network Policies in Kubernetes.
Visit Now: https://www.dumps4less.com/KCSA-dumps-pdf.html
QUESTION: 29
What is the primary purpose of implementing the NIST Cybersecurity Framework in a Kubernetes
environment?
Option A : To improve the scalability and flexibility of Kubernetes applications
Option B : To provide a structured approach for identifying, assessing, and managing cybersecurity risks
in Kubernetes
Option C : To accelerate the development cycle of applications running on Kubernetes
Option D : To enhance collaboration and communication within Kubernetes development teams
Correct Answer: B
Explanation/Reference:
Explanation: The primary purpose of implementing the NIST Cybersecurity Framework in a Kubernetes environment is to
provide a structured approach for identifying, assessing, and managing cybersecurity risks. The framework offers guidelines
and best practices to help organizations understand their cybersecurity posture, prioritize actions based on risks, and
continuously improve their security measures. In Kubernetes, this means ensuring that the container orchestration is secure,