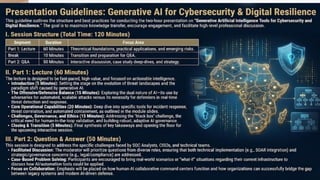
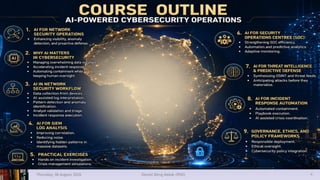
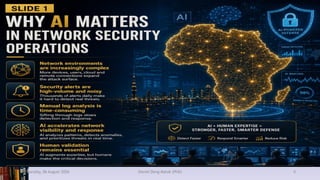
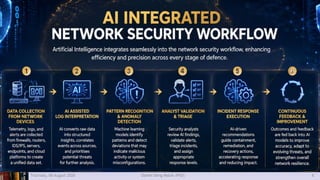
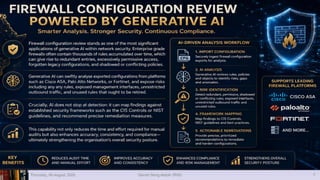
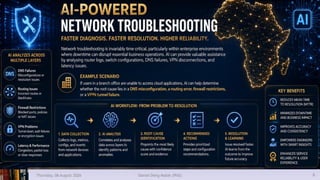
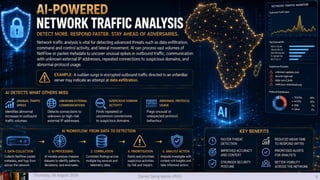
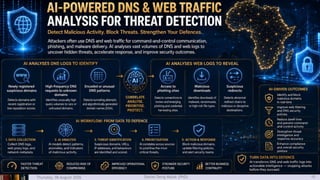
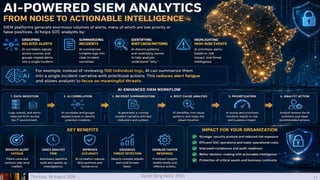
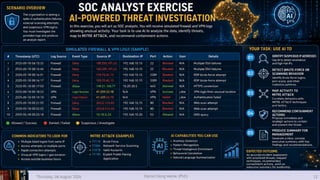
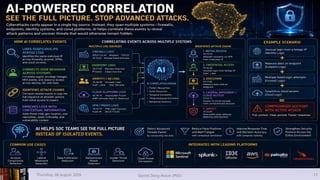
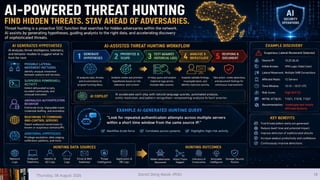
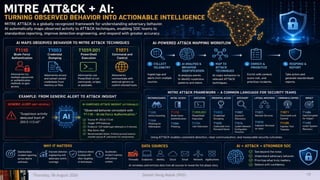
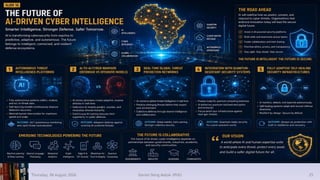
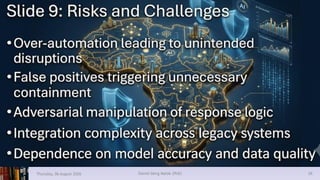
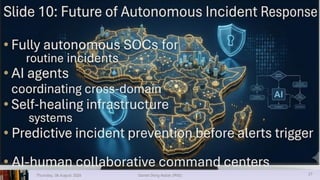
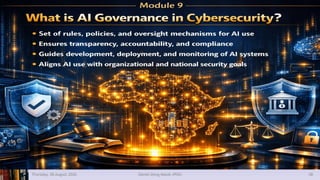
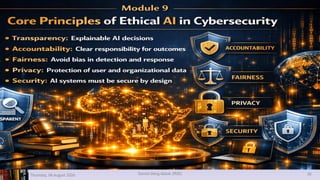
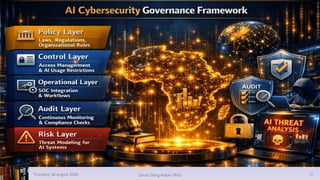
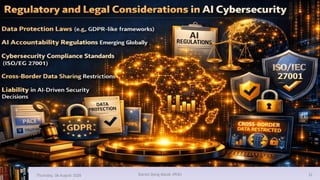
This is part two of an introductory course in using generative artificial intelligence (AI) tools for cybersecurity threat intelligence, network defence, and forensic investigations. These tools should be used according to national regulations and organizational data governance policies and guidelines. There is also the need to be cognizant of the international data protection guidelines such as the European Union (EU) AI Act, the EU General Data Protection Regulation (GDPR), the African Union (AU) Convention on Cyber Security and Personal Data Protection (Malabo Convention), the AU Data Policy Framework, the Council of Europe Convention on Cybercrime (Budapest Convention), the Organisation for Economic Co-operation and Development (OECD) Data Governance Principles, the Asia-Pacific Economic Cooperation (APEC) Cross-Border Privacy Rules (CBPR), and the National Institute of Standards and Technology (NIST)—Cybersecurity Framework (CSF 2.0).