Software Supply
Chain Security
Alex Rybak
Sr. Director, Product Management
Today’s Topics 2
1 The “threat landscape”
2 The “compliance crunch”
3 The “security tax”
5 The “key takeaways”
4 The “strategic roadmap”
The “threat landscape”
Industry trends
3
Software supply chain security (SSCS) has grown from a niche concern into a top enterprise
priority with market revenue at $2.8B+ and expected to grow to $5B+ by 2030 1
● Regulations drive product roadmaps: the EU CRA, financial and medical regulations, and
FedRAMP are driving needs for attestations, SBOM/VEX ingestion, and audit-ready evidence
● A strategic pivot from periodic scanning to continuous processes embedded in dev toolchains
● Broad adoption of SBOMs and attestations as minimum compliance artifacts
● Vulnerability triage favors exploitability analysis and runtime reachability rather than raw scores
● Paranoia around all things AI: interest in controls for AI assets and LLM supply chains including
discovery, governance, and lineage
● Massive expansion of the attack plane: shifted from simple OSS package exploitation to deep
infrastructure targeting (CI/CD pipelines, build systems, dev tools, and misconfigured IaC); recent
attacks where a firm’s AI hacked another company 2 3
(1) Gartner Magic Quadrant for Software Supply Chain Security
(2) OpenAI and Hugging Face partner to address security incident during model evaluation
(3) Meta becomes latest firm to say its AI hacked another company
The “threat landscape”
Attacks are increasing exponentially and are more sophisticated
4
1. https://beazley.security/insights/quarterly-threat-report-first-quarter-2026
2. https://modall.ca/blog/ai-in-software-development-trends-statistics
3. https://www.vulncheck.com/blog/ai-assisted-vulnerability-discovery
4. Anchore CRA webinar survey (2026)
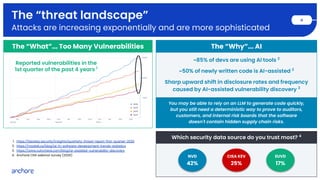
The “What”... Too Many Vulnerabilities
Reported vulnerabilities in the
1st quarter of the past 4 years 1
~85% of devs are using AI tools 2
~50% of newly written code is AI-assisted 2
Sharp upward shift in disclosure rates and frequency
caused by AI-assisted vulnerability discovery 3
The “Why”... AI
You may be able to rely on an LLM to generate code quickly,
but you still need a deterministic way to prove to auditors,
customers, and internal risk boards that the software
doesn't contain hidden supply chain risks.
NVD
42%
CISA KEV
25%
EUVD
17%
Which security data source do you trust most? 4
The “threat landscape”
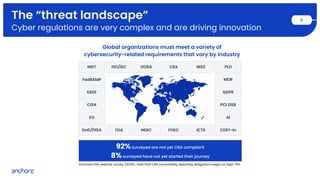
Cyber regulations are very complex and are driving innovation
5
Global organizations must meet a variety of
cybersecurity-related requirements that vary by industry
NIST
FedRAMP
CISA
SSDF
EO
ICTS
FDA
PCI DSS
NERC FFIEC
DORA CRA PLD
NIS2
MDR
GDPR
AI
CERT-In
ISO/IEC
DoD/DISA
92% surveyed are not yet CRA compliant
8% surveyed have not yet started their journey
Anchore CRA webinar survey (2026); note that CRA vulnerability reporting obligations begin on Sept. 11th
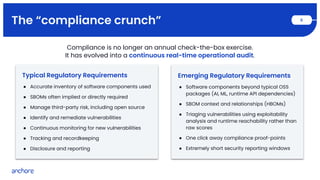
The “compliance crunch” 6
Typical Regulatory Requirements
● Accurate inventory of software components used
● SBOMs often implied or directly required
● Manage third-party risk, including open source
● Identify and remediate vulnerabilities
● Continuous monitoring for new vulnerabilities
● Tracking and recordkeeping
● Disclosure and reporting
Emerging Regulatory Requirements
● Software components beyond typical OSS
packages (AI, ML, runtime API dependencies)
● SBOM context and relationships (HBOMs)
● Triaging vulnerabilities using exploitability
analysis and runtime reachability rather than
raw scores
● One click away compliance proof-points
● Extremely short security reporting windows
Compliance is no longer an annual check-the-box exercise.
It has evolved into a continuous real-time operational audit.
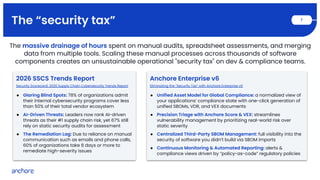
The “security tax” 7
2026 SSCS Trends Report
Security Scorecard: 2026 Supply Chain Cybersecurity Trends Report
● Glaring Blind Spots: 78% of organizations admit
their internal cybersecurity programs cover less
than 50% of their total vendor ecosystem
● AI-Driven Threats: Leaders now rank AI-driven
threats as their #1 supply chain risk, yet 67% still
rely on static security audits for assessment
● The Remediation Lag: Due to reliance on manual
communication such as emails and phone calls,
60% of organizations take 8 days or more to
remediate high-severity issues
The massive drainage of hours spent on manual audits, spreadsheet assessments, and merging
data from multiple tools. Scaling these manual processes across thousands of software
components creates an unsustainable operational "security tax" on dev & compliance teams.
Anchore Enterprise v6
Eliminating the “Security Tax” with Anchore Enterprise v6
● Unified Asset Model for Global Compliance: a normalized view of
your applications’ compliance state with one-click generation of
unified SBOMs, VDR, and VEX documents
● Precision Triage with Anchore Score & VEX: streamlines
vulnerability management by prioritizing real-world risk over
static severity
● Centralized Third-Party SBOM Management: full visibility into the
security of software you didn’t build via SBOM imports
● Continuous Monitoring & Automated Reporting: alerts &
compliance views driven by “policy-as-code” regulatory policies
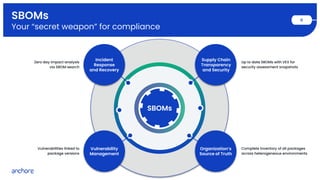
SBOMs
Your “secret weapon” for compliance
8
Up to date SBOMs with VEX for
security assessment snapshots
Complete inventory of all packages
across heterogeneous environments
Zero day impact analysis
via SBOM search
Vulnerabilities linked to
package versions
SBOMs
Supply Chain
Transparency
and Security
Organization’s
Source of Truth
Incident
Response
and Recovery
Vulnerability
Management
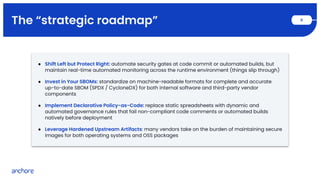
The “strategic roadmap” 9
● Shift Left but Protect Right: automate security gates at code commit or automated builds, but
maintain real-time automated monitoring across the runtime environment (things slip through)
● Invest in Your SBOMs: standardize on machine-readable formats for complete and accurate
up-to-date SBOM (SPDX / CycloneDX) for both internal software and third-party vendor
components
● Implement Declarative Policy-as-Code: replace static spreadsheets with dynamic and
automated governance rules that fail non-compliant code comments or automated builds
natively before deployment
● Leverage Hardened Upstream Artifacts: many vendors take on the burden of maintaining secure
images for both operating systems and OSS packages
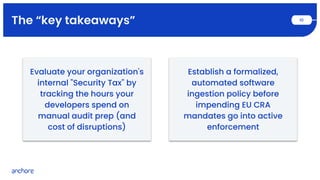
The “key takeaways” 10
Establish a formalized,
automated software
ingestion policy before
impending EU CRA
mandates go into active
enforcement
Evaluate your organization's
internal "Security Tax" by
tracking the hours your
developers spend on
manual audit prep (and
cost of disruptions)
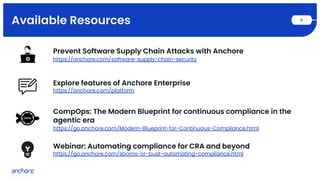
Available Resources 11
CompOps: The Modern Blueprint for continuous compliance in the
agentic era
https://go.anchore.com/Modern-Blueprint-for-Continuous-Compliance.html
Explore features of Anchore Enterprise
https://anchore.com/platform
Prevent Software Supply Chain Attacks with Anchore
https://anchore.com/software-supply-chain-security
Webinar: Automating compliance for CRA and beyond
https://go.anchore.com/sboms-or-bust-automating-compliance.html
© 2026
sales@anchore.com anchore.com
Thank you!