Comprehensive Guide to Vulnerability Remediation and Incident Response Workflow
Explore the end-to-end process from vulnerability detection to containment, remediation, and recovery, including risk assessment, prioritization, and validation techniques.
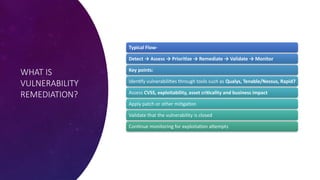
WHAT IS
VULNERABILITY
REMEDIATION?
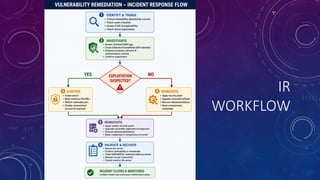
Typical Flow-
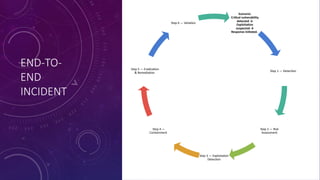
Detect→ Assess → Prioritize → Remediate → Validate → Monitor
Key points:
Identify vulnerabilities through tools such as Qualys, Tenable/Nessus, Rapid7
Assess CVSS, exploitability, asset criticality and business impact
Apply patch or other mitigation
Validate that the vulnerability is closed
Continue monitoring for exploitation attempts
KEY TAKEAWAYS /LESSONS
LEARNED
• 5 Key Takeaways
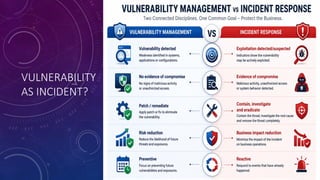
• Not every vulnerability is an incident.
• Prioritize vulnerabilities based on risk + exploitability + asset
criticality.
• If exploitation is suspected, move from vulnerability
management to incident response.
• Use SIEM + EDR + vulnerability management together for
effective detection and response.
• After remediation, always validate through rescanning and
monitoring.