Download as PDF, PPTX
- 1 / 41
- 2 / 41
- 3 / 41
- 4 / 41
- 5 / 41
- 6 / 41
- 7 / 41
- 8 / 41
- 9 / 41
- 10 / 41
- 11 / 41
- 12 / 41
- 13 / 41
- 14 / 41
- 15 / 41
- 16 / 41
- 17 / 41
- 18 / 41
- 19 / 41
- 20 / 41
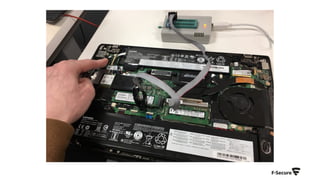
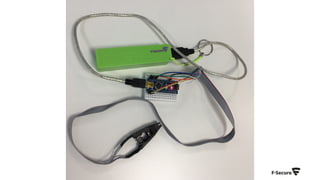
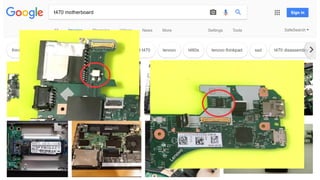

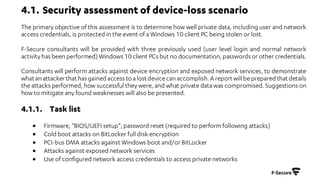
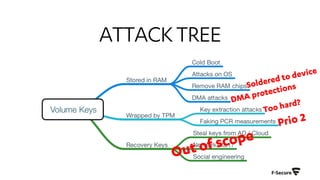
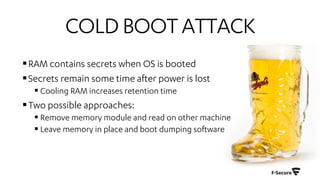
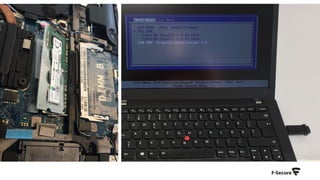
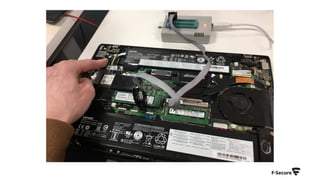
The document discusses cold boot attacks that exploit the retention of secrets in RAM after power loss, presenting two methods for data retrieval. It highlights the inadequacy of current security measures, including Secure Boot and BIOS protections, in preventing such attacks, especially in sleep mode. Recommendations include keeping firmware updated, using effective mitigations, and assessing the risks of potential disk encryption breaches.


