© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Amazon Web Services Japan K.K.
Partner Solutions Architect
Takanori Ohba
AWS における
モニタリングとセキュリティの基本について
~ 毎日のAWSのための監視、運用、セキュリティ最適化セミナー ~
2019/10/4
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Who am I ?
p 名前
Ø⼤場 崇令 (オオバ タカノリ)
p Role
ØSolutions Architect
@Amazon Web Services Japan K.K.
(Joined 2015/12)
p Background
ØAWS テクニカルトレーナー@AWSJ K.K.
ØWeb サービスのインフラエンジニア
Ø国内クラウドベンダーにてテクニカルサポート
p 好きな AWS サービス
ØAWS Systems Manager
ØAWS Server Migration Service
Ø AWS Service Catalog
@takaohba
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Agenda
p What is AWS?
p クラウドにおけるモニタリングの課題
p クラウドでチェックすべき代表的な監視項⽬
p AWS におけるセキュリティの考え⽅
p まとめ
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
What is AWS?
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
What is AWS?
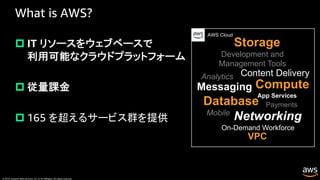
p IT リソースをウェブベースで
利用可能なクラウドプラットフォーム
p 従量課金
p 165 を超えるサービス群を提供
ComputeMessaging
Mobile
App Services
Database
Networking
Development and
Management Tools
Payments
VPC
On-Demand Workforce
Analytics Content Delivery
Storage
AWS Cloud
Our Vision:
地球上で、もっともお客様を
⼤切にする企業であること
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
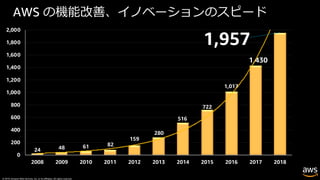
24 48 61 82
159
280
516
722
1,017
1,430
1,957
0
200
400
600
800
1,000
1,200
1,400
1,600
1,800
2,000
2008 2009 2010 2011 2012 2013 2014 2015 2016 2017 2018
AWS の機能改善、イノベーションのスピード
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
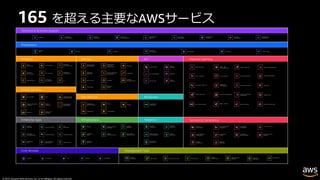
165 を超える主要なAWSサービス
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
国内における AWS 利⽤の広がり
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
今日お話しすること
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
今日お話しすること
p クラウドでチェックすべきモニタリング項目
p AWS におけるガードレール的セキュリティ
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
クラウドにおけるモニタリングの課題
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
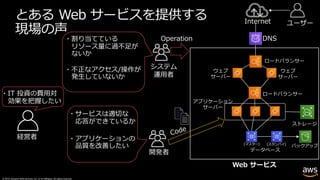
とある Web サービスを提供する
現場の声
・割り当てている
リソース量に過不⾜が
ないか
・不正なアクセス/操作が
発⽣していないか
・サービスは適切な
応答ができているか
・アプリケーションの
品質を改善したい
ウェブ
サーバー
ストレージ
ロードバランサー
データベース
バックアップ
ロードバランサー
DNS
Internet ユーザー
システム
運⽤者
開発者
アプリケーション
サーバー
Operation
Code
ウェブ
サーバー
Web サービス
(マスター) (スタンバイ)
経営者
・IT 投資の費⽤対
効果を把握したい
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
何をモニタリングする必要があるのか︖
Ø 1. カスタマーエクスペリエンス
Ø 2. パフォーマンス
Ø 3. 傾向分析
Ø 4. セキュリティ
Ø 5. コスト
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
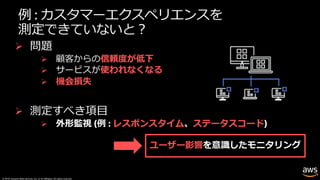
例 : カスタマーエクスペリエンスを
測定できていないと︖
Ø 問題
Ø 顧客からの信頼度が低下
Ø サービスが使われなくなる
Ø 機会損失
ユーザー影響
Ø 測定すべき項⽬
Ø 外形監視 (例 : レスポンスタイム、ステータスコード)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
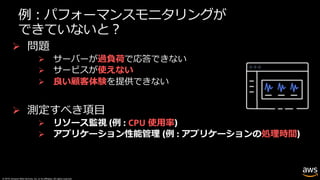
例︓パフォーマンスモニタリングが
できていないと︖
Ø 問題
Ø サーバーが過負荷で応答できない
Ø サービスが使えない
Ø 良い顧客体験を提供できない
Ø 測定すべき項⽬
Ø リソース監視 (例 : CPU 使⽤率)
Ø アプリケーション性能管理 (例 : アプリケーションの処理時間)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
例︓傾向分析ができていないと︖
Ø 問題
Ø サービスの状況に合わせた迅速な改善ができない
Ø ワークロードの課題を特定できない
Ø 測定すべき項⽬
Ø ログ監視 (例 :アクセスログからニーズの⾼いコンテンツの特定、
アプリケーションログからエラーメッセージの検出)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
例 : セキュリティモニタリングができていないと︖
Ø 問題
Ø 悪意のある第三者による不正操作
Ø 機密データの流出
Ø 測定すべき項⽬
Ø クラウド上でのアクティビティ (例 : 不審な IP アドレスからの
API の呼び出し)
Ø リソースの構成変更履歴 (例 : 逸脱する操作を検知)
Ø サービスへの脅威状況 (例 : 悪意のあるポートスキャン)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
例︓コストモニタリングができていないと︖
Ø 問題
Ø 利⽤費⽤ (コスト) の変化を検出できない
Ø 想定外の費⽤ (コスト) が発⽣
(例)︓停⽌し忘れた EC2 インスタンス (仮想サーバー) により、
無駄なコストが発⽣してしまう
Ø 測定すべき項⽬
Ø クラウドサービスの利⽤料⾦
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
クラウドで
チェックすべき代表的な監視項目
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
クラウドでチェックすべき代表的な監視項⽬
Ø 1.リソース監視
Ø パフォーマンス (例 : CPU 使⽤率)、
キャパシティ (例 : Disk 使⽤量)、
死活監視 …etc
Ø 2.ログ監視
Ø AWS サービス、OS、
アプリケーション、
ミドルウェア …etc
Ø 3.APM
(アプリケーション性能管理)
Ø リクエストの実⾏状況、
アプリケーションの問題、
処理ごとのレスポンス …etc
Ø 4.外形監視 (シンセティック監視)
Ø URL 監視、ステータスコード、
応答時間…etc
Ø 5.セキュリティ
Ø クラウド上のアクティビティ、
IT リソースへの不審な
アクティビティ…etc
Ø 6.コスト
Ø 変動する AWS サービスの利⽤費⽤
※シンセティック監視
※
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
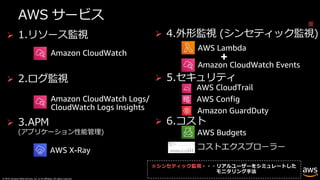
AWS サービス
Ø 1.リソース監視
Ø 2.ログ監視
Ø 3.APM
(アプリケーション性能管理)
Ø 4.外形監視 (シンセティック監視)
Ø 5.セキュリティ
Ø 6.コスト
※シンセティック監視
※
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
ここまでのまとめ
p クラウドで最低限モニタリングすべき 6 つの項⽬
Ø リソース監視、ログ監視、APM、外形監視、セキュリティ、コスト
p 各モニタリング項⽬に対して、⽀援する AWS サービス
Ø [リソース監視] Amazon CloudWatch
Ø [ログ監視] Amazon CloudWatch Logs/CloudWatch Logs Insights
Ø [APM] AWS X-Ray
Ø [外形監視] AWS Lambda + Amazon CloudWatch Events
Ø [セキュリティ] AWS Config、AWS CloudTrail、Amazon GuardDuty
Ø [コスト] コストエクスプローラー、AWS Budgets
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
[参考] AWS Summit Tokyo 2019 資料
p タイトル : クラウド環境におけるモニタリングの重要性について
Ø 資料︓https://amzn.to/2pvNCyi
Ø 動画︓https://amzn.to/2pxNdeR
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS におけるセキュリティの考え方
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
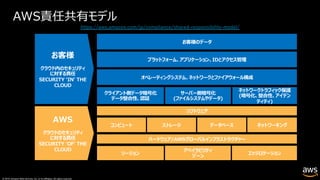
AWS責任共有モデル
https://aws.amazon.com/jp/compliance/shared-responsibility-model/
AWS
クラウドのセキュリティ
に対する責任
SECURITY ʻOFʼ THE
CLOUD
お客様
クラウド内のセキュリティ
に対する責任
SECURITY ʻINʼ THE
CLOUD
お客様のデータ
プラットフォーム、アプリケーション、IDとアクセス管理
オペレーティングシステム、ネットワークとファイアウォール構成
クライアント側データ暗号化
データ整合性、認証
サーバー側暗号化
(ファイルシステムやデータ)
ネットワークトラフィック保護
(暗号化、整合性、アイデン
ティティ)
ハードウェア/AWSグローバルインフラストラクチャー
ソフトウェア
リージョン
アベイラビリティ
ゾーン
エッジロケーション
コンピュート ストレージ データベース ネットワーキング
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Builderを⽀えるプラットフォーム
- Self Service Platform -
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
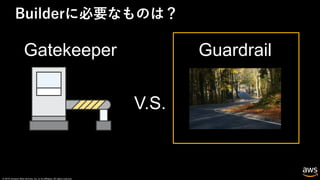
Builderに必要なものは?
Gatekeeper Guardrail
V.S.
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
ガードレールの必要性
「統制」によってブレーキをかけるのではなく、
道の外にはみ出ることだけはないようにして、
柔軟に運転を楽しんでもらおうという考え⽅
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS Config
AWS Marketplace
AWS CloudTrail
AWS Systems Manager
AWS CloudFormation
AWS Service Catalog
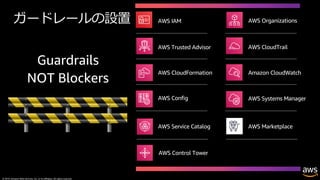
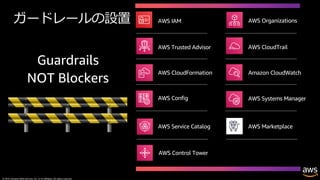
Guardrails
NOT Blockers
AWS Trusted Advisor
Amazon CloudWatch
ガードレールの設置
AWS Control Tower
AWS IAM AWS Organizations
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS Config
AWS Marketplace
AWS CloudTrail
AWS Systems Manager
AWS CloudFormation
AWS Service Catalog
Guardrails
NOT Blockers
AWS Trusted Advisor
Amazon CloudWatch
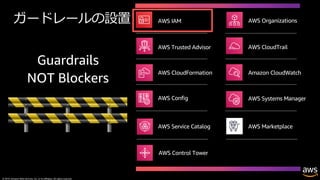
ガードレールの設置
AWS Control Tower
AWS IAM AWS Organizations
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS アカウントについて
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
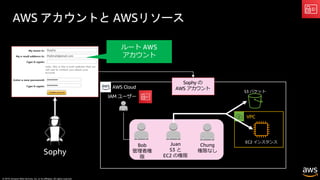
AWS Cloud
AWS アカウントと AWSリソース
Sophy の
AWS アカウント
IAM ユーザー
Bob
管理者権
限
Juan
S3 と
EC2 の権限
Chung
権限なし
EC2 インスタンス
S3 バケット
Sophy
ルート AWS
アカウント
VPC
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS IAM
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS Identity and Access Management (IAM)
お客様のAWS リソースに対するユーザーのアクセスと認証を集中管理する
p AWS アカウントの機能として無料提供
p ユーザー、グループ、ロールを作成し、
ポリシーを適⽤して AWS リソースへのアクセスを制御
p ユーザーがアクセスできるリソースと
そのアクセス⽅法を管理 (例: EC2 インスタンスの終了)
p コンテキストに基づいて必要な認証情報を定義
(例: 誰が、どのサービスにアクセスして、何をするか)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
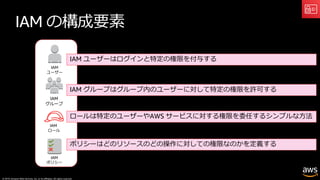
IAM の構成要素
IAM
ポリシー
IAM
ユーザー
IAM
グループ
IAM
ロール
ポリシーはどのリソースのどの操作に対しての権限なのかを定義する
ロールは特定のユーザーやAWS サービスに対する権限を委任するシンプルな⽅法
IAM ユーザーはログインと特定の権限を付与する
IAM グループはグループ内のユーザーに対して特定の権限を許可する
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
ガードレールを実現するパーミッション (IAM)
p IAM ポリシー (アイデンティティベース)
p Permissions Boundaries for IAM Entities
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
IAM ポリシー
IAM ポリシーは、1 つまたは
複数のアクセス許可を⽰す正式なステートメントである
p ユーザー、グループ、ロールといった IAM エンティティにポリシーをアタッチする
p ポリシーにより、エンティティが実⾏できるアクションが許可される
Ø 詳細なアクセス制御が有効となる
p 単⼀のポリシーを複数のエンティティにアタッチできる
p 単⼀のエンティティに複数のポリシーをアタッチできる
ベストプラクティス: 複数の IAM ユーザーに同じポリシーをアタッチする場合は、
グループにユーザーを⼊れ、ポリシーをグループにアタッチする
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
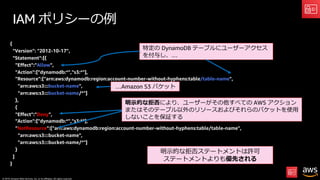
IAM ポリシーの例
{
"Version": "2012-10-17",
"Statement":[{
"Effect":"Allow",
"Action":["dynamodb:*","s3:*"],
"Resource":["arn:aws:dynamodb:region:account-number-without-hyphens:table/table-name",
"arn:aws:s3:::bucket-name",
"arn:aws:s3:::bucket-name/*"]
},
{
"Effect":"Deny",
"Action":["dynamodb:*","s3:*"],
"NotResource":["arn:aws:dynamodb:region:account-number-without-hyphens:table/table-name",
"arn:aws:s3:::bucket-name",
"arn:aws:s3:::bucket-name/*"]
}
]
}
特定の DynamoDB テーブルにユーザーアクセス
を付与し、…
明⽰的な拒否ステートメントは許可
ステートメントよりも優先される
…Amazon S3 バケット
明⽰的な拒否により、ユーザーがその他すべての AWS アクション
またはそのテーブル以外のリソースおよびそれらのバケットを使⽤
しないことを保証する
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
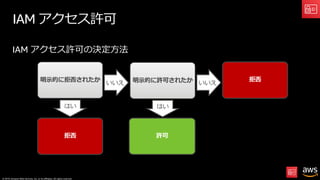
IAM アクセス許可
IAM アクセス許可の決定⽅法
明⽰的に拒否されたか いいえ
拒否
明⽰的に許可されたか
許可
拒否
はい
いいえ
はい
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
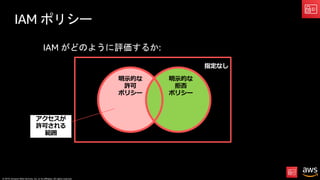
IAM ポリシー
IAM がどのように評価するか:
指定なし
明⽰的な
許可
ポリシー
明⽰的な
拒否
ポリシー
アクセスが
許可される
範囲
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
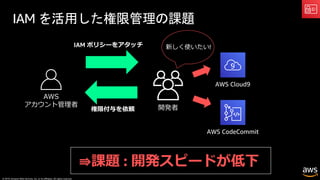
IAM を活用した権限管理の課題
開発者
AWS
アカウント管理者
AWS Cloud9
AWS CodeCommit
新しく使いたい!
権限付与を依頼
⇛課題 : 開発スピードが低下
IAM ポリシーをアタッチ
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Permissions Boundaries
for IAM Entities の概要
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
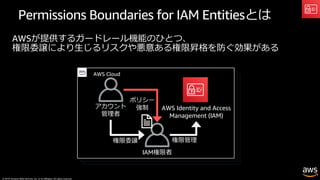
Permissions Boundaries for IAM Entitiesとは
AWSが提供するガードレール機能のひとつ、
権限委譲により⽣じるリスクや悪意ある権限昇格を防ぐ効果がある
AWS Cloud
AWS Identity and Access
Management (IAM)
権限委譲
アカウント
管理者
IAM権限者
権限管理
ポリシー
強制
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
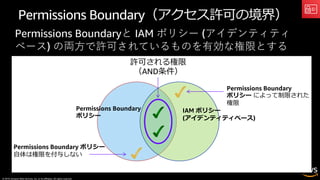
Permissions Boundary(アクセス許可の境界)
Permissions Boundaryと IAM ポリシー (アイデンティティ
ベース) の両⽅で許可されているものを有効な権限とする
Permissions Boundary
ポリシー
IAM ポリシー
(アイデンティティベース)
許可される権限
(AND条件)
Permissions Boundary ポリシー
⾃体は権限を付与しない
Permissions Boundary
ポリシー によって制限された
権限
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
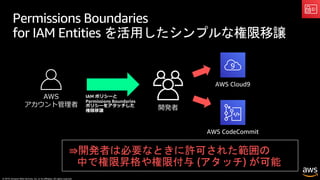
Permissions Boundaries
for IAM Entities を活用したシンプルな権限移譲
開発者
AWS
アカウント管理者
AWS Cloud9
AWS CodeCommit
IAM ポリシーと
Permissions Boundaries
ポリシーをアタッチした
権限移譲
⇛開発者は必要なときに許可された範囲の
中で権限昇格や権限付与 (アタッチ) が可能
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
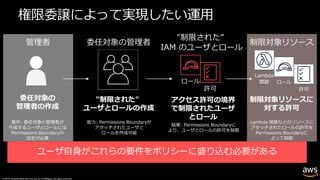
権限委譲によって実現したい運⽤
要件: 委任対象の管理者が
作成するユーザとロールには
Permissions Boundaryの
設定が必要
能⼒: Permissions Boundaryが
アタッチされたユーザと
ロールを作成可能
管理者 委任対象の管理者
"制限された”
IAM のユーザとロール
委任対象の
管理者の作成
"制限された"
ユーザとロールの作成
アクセス許可の境界
で制限されたユーザ
とロール
結果: Permissions Boundaryに
より、ユーザとロールの許可を制限
制限対象リソース
制限対象リソースに
対する許可
Lambda 関数などのリソースに
アタッチされたロールの許可を
Permissions Boundaryに
よって制限
ロール
許可
Lambda
関数 ロール
許可
ユーザ⾃⾝がこれらの要件をポリシーに盛り込む必要がある
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
AWS Config
AWS Marketplace
AWS CloudTrail
AWS Systems Manager
AWS CloudFormation
AWS Service Catalog
Guardrails
NOT Blockers
AWS Trusted Advisor
Amazon CloudWatch
ガードレールの設置
AWS Control Tower
AWS IAM AWS Organizations
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
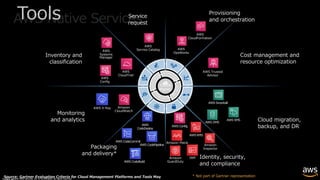
AWS Native Services
Cloud
Mgmt.
AWS
Service Catalog
AWS
CloudTrail
AWS
Config
AWS Trusted
Advisor
AWS X-Ray
AWS
OpsWorks
Amazon
CloudWatch
AWS
CloudFormation
AWS Snowball
AWS SMS
AWS
Systems
Manager
AWS KMS
IAM
AWS DMS
Amazon
Inspector
Amazon Macie
Amazon
GuardDuty
Service
request
Inventory and
classification
Monitoring
and analytics
Packaging
and delivery*
Provisioning
and orchestration
Cost management and
resource optimization
Cloud migration,
backup, and DR
Identity, security,
and compliance
AWS ConfigAWS
CodeDeploy
AWS CodeCommit
AWS CodePipeline
AWS CodeBuild
* Not part of Gartner representationSource: Gartner Evaluation Criteria for Cloud Management Platforms and Tools May
Tools
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
サードパーティ & オープンソースソリューション
+ THOUSANDS MORE ON THE AWS MARKETPLACE
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
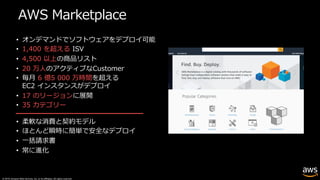
AWS Marketplace
• オンデマンドでソフトウェアをデプロイ可能
• 1,400 を超える ISV
• 4,500 以上の商品リスト
• 20 万⼈のアクティブなCustomer
• 毎⽉ 6 億5 000 万時間を超える
EC2 インスタンスがデプロイ
• 17 のリージョンに展開
• 35 カテゴリー
• 柔軟な消費と契約モデル
• ほとんど瞬時に簡単で安全なデプロイ
• ⼀括請求書
• 常に進化
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
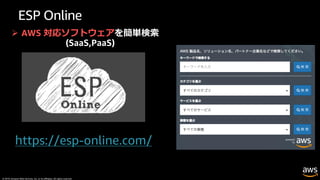
ESP Online
https://esp-online.com/
Ø AWS 対応ソフトウェアを簡単検索
(SaaS,PaaS)
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
まとめ
p AWS の紹介
p クラウドでチェックすべき
代表的な 6 つの監視項⽬と AWS サービス
p AWS におけるセキュリティの考え⽅
p ガードレールを実現するパーミッション
© 2019, Amazon Web Services, Inc. or its affiliates. All rights reserved.
Thank you!