10 Safe Ways to Manage Multiple Gmail
Accounts (Without Getting Suspended)
Managing multiple Google accounts has become standard operational practice for digital
marketers, agency owners, freelance professionals, e-commerce sellers, and corporate
teams. Whether you are segmenting customer outreach campaigns, separating brand
entities, isolating personal and business communication, or running multi-channel marketing
workflows, relying on a single Gmail inbox is rarely viable.
However, operating multiple accounts simultaneously comes with strict technical challenges.
Google utilizes sophisticated automated security systems—evaluating behavioral heuristics,
device fingerprints, network consistency, and IP reputations—to detect suspicious activity
and enforce its terms of service. An improper setup can trigger account verifications (PV
loops), temporary locks, shadowbans, or permanent suspensions.
This comprehensive guide covers the technical architecture behind Google’s security filters
and details 10 proven, secure strategies to manage multiple Gmail accounts efficiently
while maintaining high deliverability, security, and account trust.
The Technical Reality: How Google Evaluates Multiple
Accounts
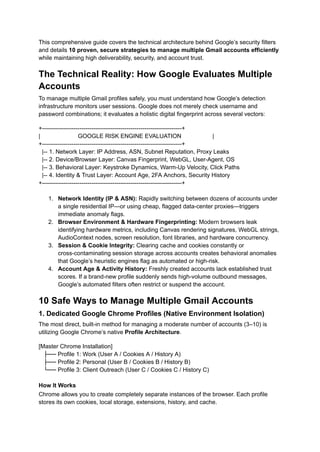
To manage multiple Gmail profiles safely, you must understand how Google’s detection
infrastructure monitors user sessions. Google does not merely check username and
password combinations; it evaluates a holistic digital fingerprint across several vectors:
+-----------------------------------------------------------------------+
| GOOGLE RISK ENGINE EVALUATION |
+-----------------------------------------------------------------------+
|-- 1. Network Layer: IP Address, ASN, Subnet Reputation, Proxy Leaks
|-- 2. Device/Browser Layer: Canvas Fingerprint, WebGL, User-Agent, OS
|-- 3. Behavioral Layer: Keystroke Dynamics, Warm-Up Velocity, Click Paths
|-- 4. Identity & Trust Layer: Account Age, 2FA Anchors, Security History
+-----------------------------------------------------------------------+
1.​ Network Identity (IP & ASN): Rapidly switching between dozens of accounts under
a single residential IP—or using cheap, flagged data-center proxies—triggers
immediate anomaly flags.
2.​ Browser Environment & Hardware Fingerprinting: Modern browsers leak
identifying hardware metrics, including Canvas rendering signatures, WebGL strings,
AudioContext nodes, screen resolution, font libraries, and hardware concurrency.
3.​ Session & Cookie Integrity: Clearing cache and cookies constantly or
cross-contaminating session storage across accounts creates behavioral anomalies
that Google’s heuristic engines flag as automated or high-risk.
4.​ Account Age & Activity History: Freshly created accounts lack established trust
scores. If a brand-new profile suddenly sends high-volume outbound messages,
Google’s automated filters often restrict or suspend the account.
10 Safe Ways to Manage Multiple Gmail Accounts
1. Dedicated Google Chrome Profiles (Native Environment Isolation)
The most direct, built-in method for managing a moderate number of accounts (3–10) is
utilizing Google Chrome’s native Profile Architecture.
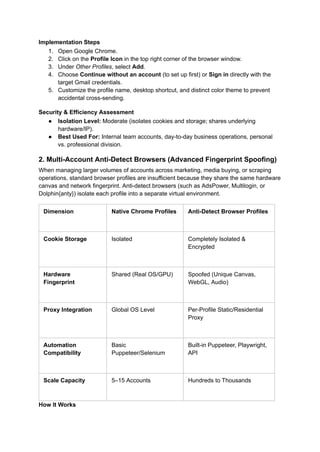
[Master Chrome Installation]
├── Profile 1: Work (User A / Cookies A / History A)
├── Profile 2: Personal (User B / Cookies B / History B)
└── Profile 3: Client Outreach (User C / Cookies C / History C)
How It Works
Chrome allows you to create completely separate instances of the browser. Each profile
stores its own cookies, local storage, extensions, history, and cache.
Implementation Steps
1.​ Open Google Chrome.
2.​ Click on the Profile Icon in the top right corner of the browser window.
3.​ Under Other Profiles, select Add.
4.​ Choose Continue without an account (to set up first) or Sign in directly with the
target Gmail credentials.
5.​ Customize the profile name, desktop shortcut, and distinct color theme to prevent
accidental cross-sending.
Security & Efficiency Assessment
●​ Isolation Level: Moderate (isolates cookies and storage; shares underlying
hardware/IP).
●​ Best Used For: Internal team accounts, day-to-day business operations, personal
vs. professional division.
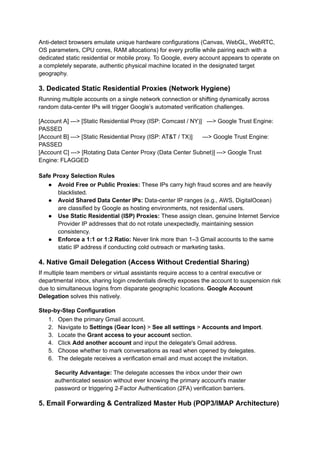
2. Multi-Account Anti-Detect Browsers (Advanced Fingerprint Spoofing)
When managing larger volumes of accounts across marketing, media buying, or scraping
operations, standard browser profiles are insufficient because they share the same hardware
canvas and network fingerprint. Anti-detect browsers (such as AdsPower, Multilogin, or
Dolphin{anty}) isolate each profile into a separate virtual environment.
Dimension Native Chrome Profiles Anti-Detect Browser Profiles
Cookie Storage Isolated Completely Isolated &
Encrypted
Hardware
Fingerprint
Shared (Real OS/GPU) Spoofed (Unique Canvas,
WebGL, Audio)
Proxy Integration Global OS Level Per-Profile Static/Residential
Proxy
Automation
Compatibility
Basic
Puppeteer/Selenium
Built-in Puppeteer, Playwright,
API
Scale Capacity 5–15 Accounts Hundreds to Thousands
How It Works
Anti-detect browsers emulate unique hardware configurations (Canvas, WebGL, WebRTC,
OS parameters, CPU cores, RAM allocations) for every profile while pairing each with a
dedicated static residential or mobile proxy. To Google, every account appears to operate on
a completely separate, authentic physical machine located in the designated target
geography.
3. Dedicated Static Residential Proxies (Network Hygiene)
Running multiple accounts on a single network connection or shifting dynamically across
random data-center IPs will trigger Google’s automated verification challenges.
[Account A] ---> [Static Residential Proxy (ISP: Comcast / NY)] ---> Google Trust Engine:
PASSED
[Account B] ---> [Static Residential Proxy (ISP: AT&T / TX)] ---> Google Trust Engine:
PASSED
[Account C] ---> [Rotating Data Center Proxy (Data Center Subnet)] ---> Google Trust
Engine: FLAGGED
Safe Proxy Selection Rules
●​ Avoid Free or Public Proxies: These IPs carry high fraud scores and are heavily
blacklisted.
●​ Avoid Shared Data Center IPs: Data-center IP ranges (e.g., AWS, DigitalOcean)
are classified by Google as hosting environments, not residential users.
●​ Use Static Residential (ISP) Proxies: These assign clean, genuine Internet Service
Provider IP addresses that do not rotate unexpectedly, maintaining session
consistency.
●​ Enforce a 1:1 or 1:2 Ratio: Never link more than 1–3 Gmail accounts to the same
static IP address if conducting cold outreach or marketing tasks.
4. Native Gmail Delegation (Access Without Credential Sharing)
If multiple team members or virtual assistants require access to a central executive or
departmental inbox, sharing login credentials directly exposes the account to suspension risk
due to simultaneous logins from disparate geographic locations. Google Account
Delegation solves this natively.
Step-by-Step Configuration
1.​ Open the primary Gmail account.
2.​ Navigate to Settings (Gear Icon) > See all settings > Accounts and Import.
3.​ Locate the Grant access to your account section.
4.​ Click Add another account and input the delegate's Gmail address.
5.​ Choose whether to mark conversations as read when opened by delegates.
6.​ The delegate receives a verification email and must accept the invitation.
Security Advantage: The delegate accesses the inbox under their own
authenticated session without ever knowing the primary account's master
password or triggering 2-Factor Authentication (2FA) verification barriers.
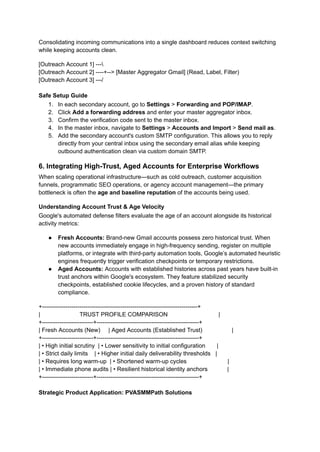
5. Email Forwarding & Centralized Master Hub (POP3/IMAP Architecture)
Consolidating incoming communications into a single dashboard reduces context switching
while keeping accounts clean.
[Outreach Account 1] ---
[Outreach Account 2] ----+--> [Master Aggregator Gmail] (Read, Label, Filter)
[Outreach Account 3] ---/
Safe Setup Guide
1.​ In each secondary account, go to Settings > Forwarding and POP/IMAP.
2.​ Click Add a forwarding address and enter your master aggregator inbox.
3.​ Confirm the verification code sent to the master inbox.
4.​ In the master inbox, navigate to Settings > Accounts and Import > Send mail as.
5.​ Add the secondary account's custom SMTP configuration. This allows you to reply
directly from your central inbox using the secondary email alias while keeping
outbound authentication clean via custom domain SMTP.
6. Integrating High-Trust, Aged Accounts for Enterprise Workflows
When scaling operational infrastructure—such as cold outreach, customer acquisition
funnels, programmatic SEO operations, or agency account management—the primary
bottleneck is often the age and baseline reputation of the accounts being used.
Understanding Account Trust & Age Velocity
Google's automated defense filters evaluate the age of an account alongside its historical
activity metrics:
●​ Fresh Accounts: Brand-new Gmail accounts possess zero historical trust. When
new accounts immediately engage in high-frequency sending, register on multiple
platforms, or integrate with third-party automation tools, Google’s automated heuristic
engines frequently trigger verification checkpoints or temporary restrictions.
●​ Aged Accounts: Accounts with established histories across past years have built-in
trust anchors within Google's ecosystem. They feature stabilized security
checkpoints, established cookie lifecycles, and a proven history of standard
compliance.
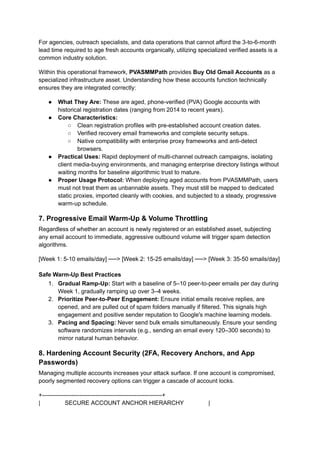
+-------------------------------------------------------------------------------+
| TRUST PROFILE COMPARISON |
+--------------------------+----------------------------------------------------+
| Fresh Accounts (New) | Aged Accounts (Established Trust) |
+--------------------------+----------------------------------------------------+
| • High initial scrutiny | • Lower sensitivity to initial configuration |
| • Strict daily limits | • Higher initial daily deliverability thresholds |
| • Requires long warm-up | • Shortened warm-up cycles |
| • Immediate phone audits | • Resilient historical identity anchors |
+--------------------------+----------------------------------------------------+
Strategic Product Application: PVASMMPath Solutions
For agencies, outreach specialists, and data operations that cannot afford the 3-to-6-month
lead time required to age fresh accounts organically, utilizing specialized verified assets is a
common industry solution.
Within this operational framework, PVASMMPath provides Buy Old Gmail Accounts as a
specialized infrastructure asset. Understanding how these accounts function technically
ensures they are integrated correctly:
●​ What They Are: These are aged, phone-verified (PVA) Google accounts with
historical registration dates (ranging from 2014 to recent years).
●​ Core Characteristics:
○​ Clean registration profiles with pre-established account creation dates.
○​ Verified recovery email frameworks and complete security setups.
○​ Native compatibility with enterprise proxy frameworks and anti-detect
browsers.
●​ Practical Uses: Rapid deployment of multi-channel outreach campaigns, isolating
client media-buying environments, and managing enterprise directory listings without
waiting months for baseline algorithmic trust to mature.
●​ Proper Usage Protocol: When deploying aged accounts from PVASMMPath, users
must not treat them as unbannable assets. They must still be mapped to dedicated
static proxies, imported cleanly with cookies, and subjected to a steady, progressive
warm-up schedule.
7. Progressive Email Warm-Up & Volume Throttling
Regardless of whether an account is newly registered or an established asset, subjecting
any email account to immediate, aggressive outbound volume will trigger spam detection
algorithms.
[Week 1: 5-10 emails/day] ──> [Week 2: 15-25 emails/day] ──> [Week 3: 35-50 emails/day]
Safe Warm-Up Best Practices
1.​ Gradual Ramp-Up: Start with a baseline of 5–10 peer-to-peer emails per day during
Week 1, gradually ramping up over 3–4 weeks.
2.​ Prioritize Peer-to-Peer Engagement: Ensure initial emails receive replies, are
opened, and are pulled out of spam folders manually if filtered. This signals high
engagement and positive sender reputation to Google's machine learning models.
3.​ Pacing and Spacing: Never send bulk emails simultaneously. Ensure your sending
software randomizes intervals (e.g., sending an email every 120–300 seconds) to
mirror natural human behavior.
8. Hardening Account Security (2FA, Recovery Anchors, and App
Passwords)
Managing multiple accounts increases your attack surface. If one account is compromised,
poorly segmented recovery options can trigger a cascade of account locks.
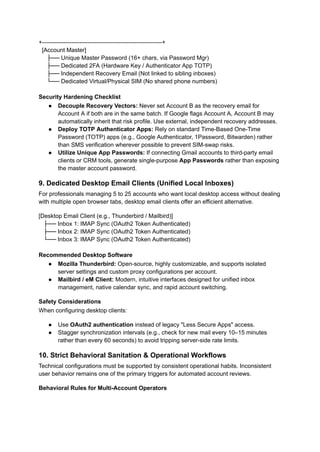
+-------------------------------------------------------------+
| SECURE ACCOUNT ANCHOR HIERARCHY |
+-------------------------------------------------------------+
[Account Master]
├── Unique Master Password (16+ chars, via Password Mgr)
├── Dedicated 2FA (Hardware Key / Authenticator App TOTP)
├── Independent Recovery Email (Not linked to sibling inboxes)
└── Dedicated Virtual/Physical SIM (No shared phone numbers)
Security Hardening Checklist
●​ Decouple Recovery Vectors: Never set Account B as the recovery email for
Account A if both are in the same batch. If Google flags Account A, Account B may
automatically inherit that risk profile. Use external, independent recovery addresses.
●​ Deploy TOTP Authenticator Apps: Rely on standard Time-Based One-Time
Password (TOTP) apps (e.g., Google Authenticator, 1Password, Bitwarden) rather
than SMS verification wherever possible to prevent SIM-swap risks.
●​ Utilize Unique App Passwords: If connecting Gmail accounts to third-party email
clients or CRM tools, generate single-purpose App Passwords rather than exposing
the master account password.
9. Dedicated Desktop Email Clients (Unified Local Inboxes)
For professionals managing 5 to 25 accounts who want local desktop access without dealing
with multiple open browser tabs, desktop email clients offer an efficient alternative.
[Desktop Email Client (e.g., Thunderbird / Mailbird)]
├── Inbox 1: IMAP Sync (OAuth2 Token Authenticated)
├── Inbox 2: IMAP Sync (OAuth2 Token Authenticated)
└── Inbox 3: IMAP Sync (OAuth2 Token Authenticated)
Recommended Desktop Software
●​ Mozilla Thunderbird: Open-source, highly customizable, and supports isolated
server settings and custom proxy configurations per account.
●​ Mailbird / eM Client: Modern, intuitive interfaces designed for unified inbox
management, native calendar sync, and rapid account switching.
Safety Considerations
When configuring desktop clients:
●​ Use OAuth2 authentication instead of legacy "Less Secure Apps" access.
●​ Stagger synchronization intervals (e.g., check for new mail every 10–15 minutes
rather than every 60 seconds) to avoid tripping server-side rate limits.
10. Strict Behavioral Sanitation & Operational Workflows
Technical configurations must be supported by consistent operational habits. Inconsistent
user behavior remains one of the primary triggers for automated account reviews.
Behavioral Rules for Multi-Account Operators
1.​ Maintain Consistent Geolocation: If an account was set up or primarily operated
from a US East Coast IP, logging into that profile from a European or Asian IP without
an intermediate transition period triggers immediate geo-velocity security flags.
2.​ Avoid Identical Email Copy Across Accounts: Distribute unique variants of
outreach copy using spintax or personalized dynamic variables. Identical message
bodies sent simultaneously across multiple accounts will trigger global spam filters.
3.​ Maintain Realistic Interaction Patterns: Authentic users browse YouTube, interact
with Google Drive, conduct Google Searches, and manage calendar events.
Interacting with the broader Google ecosystem helps maintain a natural user profile
compared to accounts used exclusively for outbound messaging.
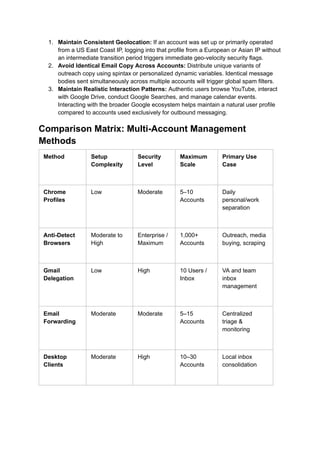
Comparison Matrix: Multi-Account Management
Methods
Method Setup
Complexity
Security
Level
Maximum
Scale
Primary Use
Case
Chrome
Profiles
Low Moderate 5–10
Accounts
Daily
personal/work
separation
Anti-Detect
Browsers
Moderate to
High
Enterprise /
Maximum
1,000+
Accounts
Outreach, media
buying, scraping
Gmail
Delegation
Low High 10 Users /
Inbox
VA and team
inbox
management
Email
Forwarding
Moderate Moderate 5–15
Accounts
Centralized
triage &
monitoring
Desktop
Clients
Moderate High 10–30
Accounts
Local inbox
consolidation
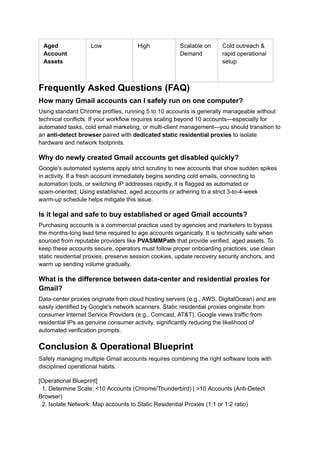
Aged
Account
Assets
Low High Scalable on
Demand
Cold outreach &
rapid operational
setup
Frequently Asked Questions (FAQ)
How many Gmail accounts can I safely run on one computer?
Using standard Chrome profiles, running 5 to 10 accounts is generally manageable without
technical conflicts. If your workflow requires scaling beyond 10 accounts—especially for
automated tasks, cold email marketing, or multi-client management—you should transition to
an anti-detect browser paired with dedicated static residential proxies to isolate
hardware and network footprints.
Why do newly created Gmail accounts get disabled quickly?
Google's automated systems apply strict scrutiny to new accounts that show sudden spikes
in activity. If a fresh account immediately begins sending cold emails, connecting to
automation tools, or switching IP addresses rapidly, it is flagged as automated or
spam-oriented. Using established, aged accounts or adhering to a strict 3-to-4-week
warm-up schedule helps mitigate this issue.
Is it legal and safe to buy established or aged Gmail accounts?
Purchasing accounts is a commercial practice used by agencies and marketers to bypass
the months-long lead time required to age accounts organically. It is technically safe when
sourced from reputable providers like PVASMMPath that provide verified, aged assets. To
keep these accounts secure, operators must follow proper onboarding practices: use clean
static residential proxies, preserve session cookies, update recovery security anchors, and
warm up sending volume gradually.
What is the difference between data-center and residential proxies for
Gmail?
Data-center proxies originate from cloud hosting servers (e.g., AWS, DigitalOcean) and are
easily identified by Google's network scanners. Static residential proxies originate from
consumer Internet Service Providers (e.g., Comcast, AT&T). Google views traffic from
residential IPs as genuine consumer activity, significantly reducing the likelihood of
automated verification prompts.
Conclusion & Operational Blueprint
Safely managing multiple Gmail accounts requires combining the right software tools with
disciplined operational habits.
[Operational Blueprint]
1. Determine Scale: <10 Accounts (Chrome/Thunderbird) | >10 Accounts (Anti-Detect
Browser)
2. Isolate Network: Map accounts to Static Residential Proxies (1:1 or 1:2 ratio)
3. Source Trust: Age accounts organically over 90+ days OR deploy aged assets via
PVASMMPath
4. Secure Infrastructure: Implement independent 2FA, decoupled recovery emails, and
OAuth2
5. Warm-Up & Throttle: Progressively scale volume from 5 to 40+ daily emails over 3-4
weeks
By isolating browser environments, maintaining network consistency with static residential
proxies, securing your authentication anchors, and choosing the right trust
baseline—whether through gradual internal aging or deploying verified aged assets from
PVASMMPath—you can build a scalable, resilient multi-account infrastructure that protects
your sender reputation and keeps your accounts active over the long term.